DNAT 转发 VPN流量到内网(udp 4500端口).note
如果拓扑中有一台(或者所有)VPN设备在内网,那么就需要配置 cisco 的DNAT,将 ipsec esp 流量转发进内网
·拓扑:
BR-R2 在内网
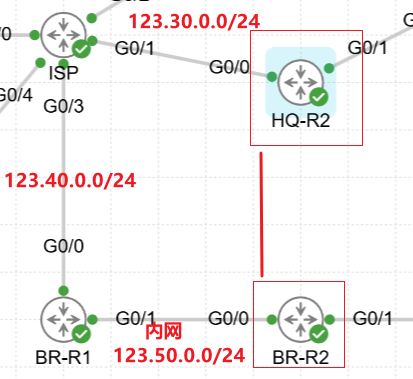
这里使用的是 GRE over IPSec(IKEv2证书加密),tunnel 类型是 ipsec ipv4
1、配置 VPN:
# 内网的VPN设备正常配置即可(VPN证书写内网设备自己的地址)
## 公网的VPN设备需要将对端IP指向DNAT的公网地址(由DNAT负责将请求转发进内网)

# HQ-R2:
interface Tunnel100

 ip address 10.0.0.1 255.255.255.252

 tunnel source GigabitEthernet0/0

 tunnel mode ipsec ipv4

 tunnel destination 123.40.0.1

 tunnel protection ipsec profile PRO

end
# ikev2 加密也是,在HQ-R2上将对端地址写为对端网关公网地址
2、BR-R1 上配置 DNAT:
# 设置nat外网接口:
interface g0/0
 ip nat outside

# 设置nat内网接口:
interface g0/1
 ip nat inside

# 设置 DNAT:
## 这里的VPN类型使用的是 UDP 4500端口
ip nat inside source static udp 123.50.0.200 4500 interface g0/0 4500
ip nat inside source static udp [内网地址] [内网端口] interface [公网接口] [公网端口]