IKEv2 证书.note
·拓扑:
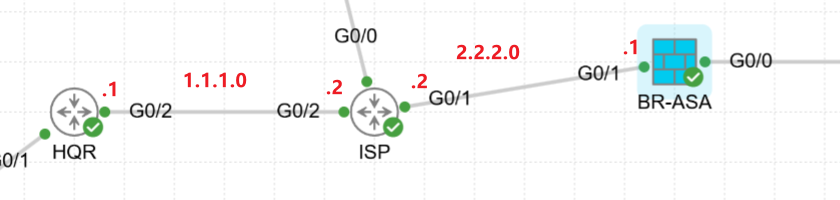
在CML 2.9中 ASA默认用了AES 128,因此定义第二阶段协商是,建议要么都是AES 128,要么就是 AES 256
1、ISP 上 配置 CA根证书颁发机构:
ntp master
ntp master 1

# 配置 根CA:
crypto key generate rsa modulus 4096 label ROOTCA

crypto pki trustpoint ROOTCA

 rsakeypair ROOTCA     // 关联证书私钥

crypto pki server ROOTCA

 grant auto

 hash sha256    //这里必须配置哈希,否则ASA证书无法生效

 lifetime ca-certificate 3650
 eku server-auth client-auth    //(可选)设置证书的使用类型

 no shutdown   // 关联好证书私钥后,再配置;

ip http server
2、ASA、路由器 申请证书:
两边之间的时间误差不能够超过10秒
# ASA:
ntp server 8.8.8.8    //与CA同步时间
crypto key generate rsa label VPN modulus 2048    //ASA一定需要本地生成一个密钥,才能够进行申请

crypto ca trustpoint VPN

 enrollment protocol scep url http://8.8.8.8:80


 subject-name cn=2.2.2.1    //注意这里不能够写多个字段

 ip-address 2.2.2.1
 fqdn none
 revocation-check none
 keypair VPN    //关联刚刚生成的私钥

crypto ca authenticate VPN
crypto ca enroll VPN
# 输入密码
# 是否包含设备名 no
# 是否申请证书 yes

# HQ-R1:
ntp server 8.8.8.8
crypto key generate rsa label VPN modulus 2048

crypto pki trustpoint VPN

 enrollment url http://8.8.8.8


 ip-address 1.1.1.1

 subject-name cn=1.1.1.1
 fqdn none

 revocation-check none
 rsakeypair VPN    //关联刚刚生成的私钥

crypto pki authenticate VPN

crypto pki enroll VPN
4、ASA配置 IKEv2:
same-security-traffic permit inter-interface

same-security-traffic permit intra-interface

crypto ikev2 enable Outside
# 设置使用地址进行协商:
crypto isakmp identity address    //如果不配置,默认会使用 主机名+域名(FQDN)进行协商
# 配置一阶段加密:
crypto ikev2 policy 1

 encryption aes-256

 integrity sha256

 group 14
 prf sha256

# 配置 第二阶段加密:
crypto ipsec ikev2 ipsec-proposal PROPOSAL

 protocol esp encryption aes-256

 protocol esp integrity sha-256

# 配置 tunnel-group:
## tunnel-group 指定对端地址
tunnel-group 1.1.1.1 type ipsec-l2l
tunnel-group 1.1.1.1 ipsec-attributes


 peer-id-validate nocheck

 ikev2 remote-authentication certificate

 ikev2 local-authentication certificate VPN    //指定本地证书的 trustpoint 名称


# 设置 ipsec profile:
crypto ipsec profile PRO

 set ikev2 ipsec-proposal PROPOSAL

 set trustpoint VPN

#配置 tunnel 接口,并应用ipsec profile:
interface Tunnel0

 nameif Tunnel

 ip address 10.0.0.2 255.255.255.252

 tunnel source interface Outside

 tunnel destination 1.1.1.1

 tunnel mode ipsec ipv4
 tunnel protection ipsec profile PRO
5、路由器 配置IKEv2:
# 配置第一阶段加密:
crypto ikev2 proposal PROPOSAL

 encryption aes-cbc-256

 integrity sha256

 group 14
 prf sha256

# 配置policy关联proposal:
crypto ikev2 policy POLICY
 proposal PROPOSAL

# 配置第二阶段加密(transform-set)
crypto ipsec transform-set IPSEC esp-aes 256 esp-sha256-hmac

 mode transport

# 配置 ikev2 profile(等同于ASA的tunnel-group)
crypto ikev2 profile PROFILE

 match identity remote any
 identity local address 1.1.1.1

 authentication remote rsa-sig

 authentication local rsa-sig

 pki trustpoint VPN

# 配置 ipsec profile:
crypto ipsec profile PRO

 set transform-set IPSEC

 set ikev2-profile PROFILE

# 关闭吊销列表(必须要敲,但是在DMVPN中就无需):
no crypto ikev2 http-url cert

# 配置 tunnel 接口,并应用 ipsec profile:
interface Tunnel100

 ip address 10.0.0.1 255.255.255.252

 tunnel source GigabitEthernet0/2

 tunnel mode ipsec ipv4

 tunnel destination 2.2.2.1
 tunnel protection ipsec profile PRO
·注意:ASA tunnel 只能够建立 BGP 动态路由,或者使用静态路由,也可以建立OSPF路由(但是要将路由器mtu设置为与ASA防火墙一致,否则无法建立)
HQ:
router bgp 2024


 network 172.16.10.0 mask 255.255.255.0

 neighbor 10.0.0.2 remote-as 2025

ASA:
router bgp 2025


 address-family ipv4 unicast

  neighbor 10.0.0.1 remote-as 2024

  neighbor 10.0.0.1 activate

  network 172.16.1.0 mask 255.255.255.0