配置以LDAP为后端进行AAA身份认证 or Auth Proxy.note
1、使用LDAP为后端进行AAA身份认证:
先在linux上正常配置好LDAP,或者在windows上配置好AD域
# 连接openLDAP:
aaa-server LDAP protocol ldap
 exit
aaa-server LDAP (inside) host 192.168.0.2
 server-port 389
 ldap-base-dn dc=rapa,dc=local    //定义用户存储路径
 # ldap-base-dn ou=NetAdmins,dc=rapa,dc=local    //可以写OU
 ldap-scope subtree
 ldap-naming-attribute uid
 ldap-login-dn cn=admin,dc=rapa,dc=local
 ldap-login-password Skills39

# 连接AD域:
aaa-server AD protocol ldap
aaa-server AD (dmz) host 192.168.0.1
 server-port 389
 ldap-base-dn dc=rapa,dc=local
 ldap-scope subtree
 ldap-naming-attribute cn
 ldap-login-dn cn=administrator,cn=users,dc=rapa,dc=local
 ldap-login-password Skills39
# 使用命令测试:
test aaa-server authentication LDAP host 192.168.0.2 username admin01 password Skills39
test aaa-server authentication LDAP username administrator password Skills39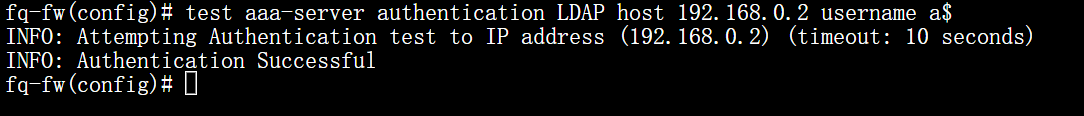
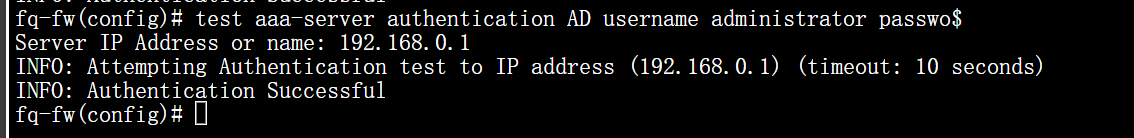
# 然后就能够在console、ssh登陆中调用了:
## 建议测试时创建一个本地用户保底,不然登陆不上就完了:username admin password Skills39
aaa authentication serial console LDAP LOCAL
aaa authentication ssh console LDAP LOCAL
·OpenLDAP 的要求:
• OpenLDAP 服务器必须位于可从 ASAv 访问的位置。
• LDAP 用户必须使用 ASAv 可访问的属性(例如:uid、cn)进行身份验证。
• 如果使用 SSL/TLS,那么 OpenLDAP 服务器的证书和 ASAv 的可信证书必须进行设置。
注意事项
• OpenLDAP 与 Cisco ASA/ASAv 的集成遵循标准的 LDAP 协议,因此使用 OpenLDAP 没有问题。
• 如果需要,可以在 LDAP 服务器上通过用户组基础的权限设置(授权)来构建更细化的策略。
在使用 Cisco ASA 和 ASAv 的 Authentication Proxy(认证代理)功能时,应将用户后端数据库设置为 OpenLDAP/AD域。
Cisco ASA 的用户认证支持与 LDAP 服务器的集成,通过这种方式,您可以使用像 OpenLDAP/AD域 这样的 LDAP 兼容目录服务作为后端服务。
设置摘要
1. LDAP 服务器配置:在 OpenLDAP 服务器上添加用户,并设置适当的访问控制列表(ACL)和结构。
2. 在 ASAv 中的 LDAP 配置:
○ 在 ASAv 中将 LDAP 服务器注册为 AAA 服务器。
○ 配置针对 LDAP 服务器的认证和搜索设置。
○ 设置在认证请求中将使用的 LDAP 字段(例如:sAMAccountName 或 uid)。
3. Auth Proxy 与 LDAP 的连接:
○ 在 Auth Proxy 中,选择使用 LDAP 进行认证。
根据 LDAP 服务器中用户的认证结果来处理权限授予事宜。2、Auth Proxy 调用LDAP后端:
直接匹配流量,将它重定向到ASA上进行一次认证
# 也是像上面一样配置 aaa-server
## 新配置:
aaa authentication listener https dmz port 443 redirect
# 然后定义一个匹配流量的规则,将匹配到的流量重定向过来:
access-list HTTPS permit tcp any any eq 443
aaa authentication match HTTPS outside LDAP    //将匹配到的流量,使用LDAP认证

## 参数解释
aaa authentication listener    //定义一个门户入口
https    //门户用https提供登陆页面
dmz    //监听在dmz nameif接口上(允许dmz nameif接口流量访问)
port 443    //监听端口443(用户认证时访问ASA的443端口)
redirect    //ASA在检测到某个流量需要认证时,将用户重定向过来


## 旧配置:
aaa authentication listener https-authen
aaa authentication listener https-authen server-group LDAP