noteId: WEB301246113204cb20b2550f7e7b953023 · 原始路径:/ALL/网络 - C模块/1-韩国专家拓扑/2-EIGRP.note · 图片:2 · 附件待处理:0
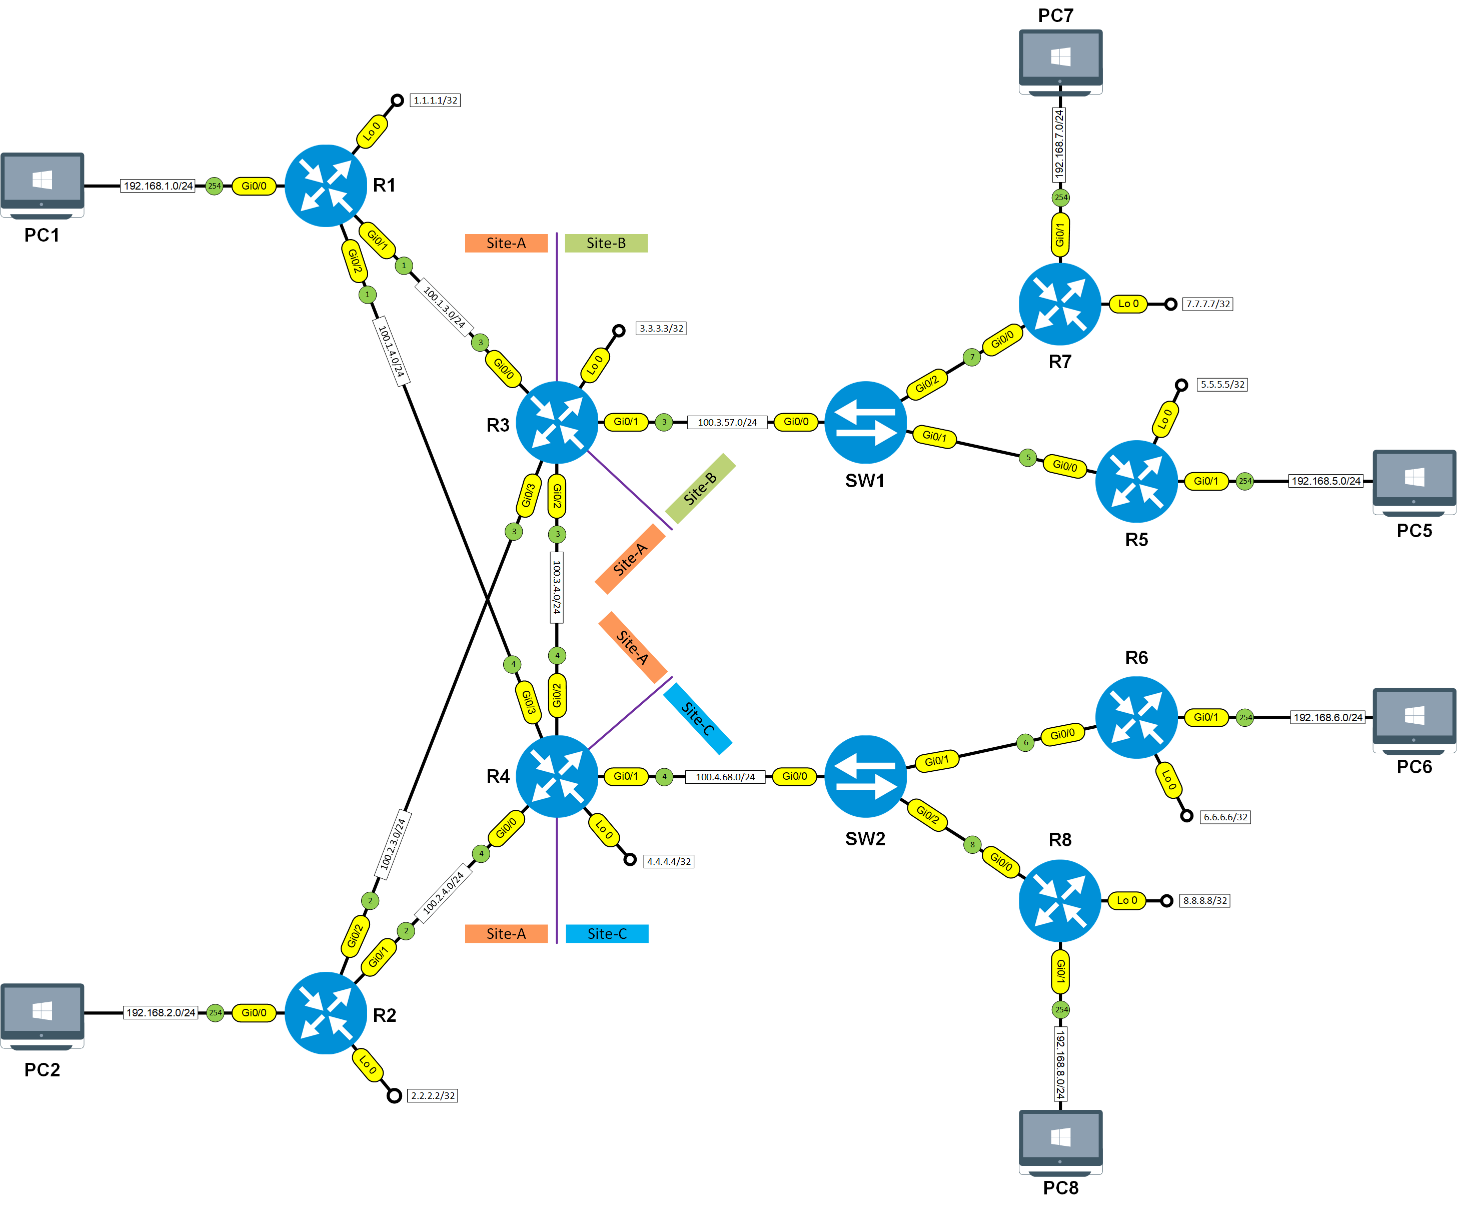
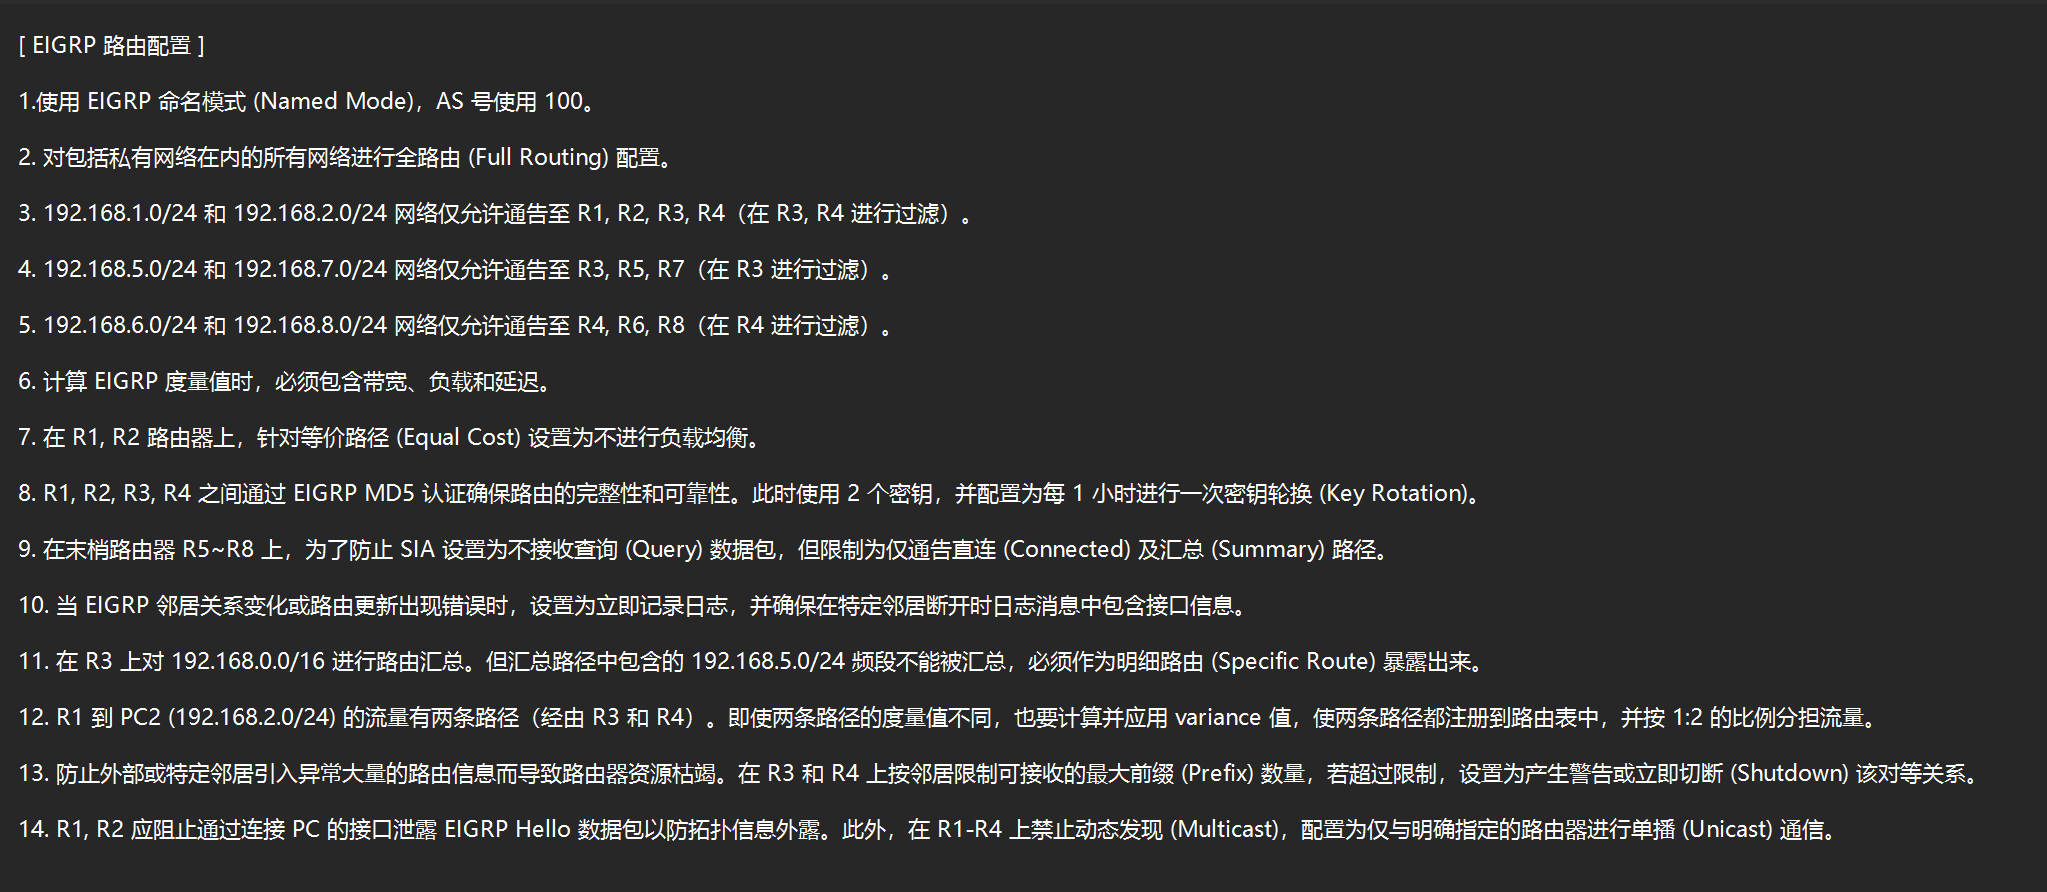
3. 192.168.1.0/24 和 192.168.2.0/24 网络仅允许通告至 R1, R2, R3, R4(在 R3, R4 进行过滤)。
# R3、4:
access-list 1 deny   192.168.1.0 0.0.0.255
access-list 1 deny   192.168.2.0 0.0.0.255
access-list 1 permit any
router eigrp 100
 distribute-list 1 out GigabitEthernet0/1

4. 192.168.5.0/24 和 192.168.7.0/24 网络仅允许通告至 R3, R5, R7(在 R3 进行过滤)。
# R3:
access-list 2 deny   192.168.5.0 0.0.0.255
access-list 2 deny   192.168.7.0 0.0.0.255
access-list 2 permit any
router eigrp 100
 distribute-list 2 out GigabitEthernet0/0
 distribute-list 2 out GigabitEthernet0/3
 distribute-list 2 out GigabitEthernet0/2

5. 192.168.6.0/24 和 192.168.8.0/24 网络仅允许通告至 R4, R6, R8(在 R4 进行过滤)。
# R4:
access-list 2 deny   192.168.6.0 0.0.0.255
access-list 2 deny   192.168.8.0 0.0.0.255
access-list 2 permit any
router eigrp 100
 distribute-list 2 out GigabitEthernet0/0
 distribute-list 2 out GigabitEthernet0/2
 distribute-list 2 out GigabitEthernet0/3

6. 计算 EIGRP 度量值时,必须包含带宽、负载和延迟。
router eigrp 100
 metric weights 0 1 1 1 0 0

7. 在 R1, R2 路由器上,针对等价路径 (Equal Cost) 设置为不进行负载均衡。
# R1、2
router eigrp 100
 maximum-paths 1

8. R1, R2, R3, R4 之间通过 EIGRP MD5 认证确保路由的完整性和可靠性。此时使用 2 个密钥,并配置为每 1 小时进行一次密钥轮换 (Key Rotation)。
key chain KEY
 key 1
  key-string Skills39
  accept-lifetime 09:00:00 May 29 2026 duration 3600
  send-lifetime 09:00:00 May 29 2026 duration 3600
  cryptographic-algorithm md5
 key 2
  key-string Skills39Skills39
  accept-lifetime 10:00:00 May 29 2026 duration 3600
  send-lifetime 10:00:00 May 29 2026 duration 3600
  cryptographic-algorithm md5

int g0/1
 ip authentication mode eigrp 100 md5
 ip authentication key-chain eigrp 100 KEY

9. 在末梢路由器 R5~R8 上,为了防止 SIA 设置为不接收查询 (Query) 数据包,但限制为仅通告直连 (Connected) 及汇总 (Summary) 路径。
router eigrp 100
 eigrp stub connected summary

10. 当 EIGRP 邻居关系变化或路由更新出现错误时,设置为立即记录日志,并确保在特定邻居断开时日志消息中包含接口信息。
router eigrp 100
 eigrp log-neighbor-changes
 eigrp log-neighbor-warnings

11. 在 R3 上对 192.168.0.0/16 进行路由汇总。但汇总路径中包含的 192.168.5.0/24 频段不能被汇总,必须作为明细路由 (Specific Route) 暴露出来。
access-list 3 permit 192.168.5.0 0.0.0.255
route-map LEAK permit 10
 match ip address 3
int g0/1
 ip summary-address eigrp 100 192.168.0.0/16 leak-map LEAK

12. R1 到 PC2 (192.168.2.0/24) 的流量有两条路径(经由 R3 和 R4)。即使两条路径的度量值不同,也要计算并应用 variance 值,使两条路径都注册到路由表中,并按 1:2 的比例分担流量。
## 这个点会与前面的(等价路径设置为不进行负载均衡)冲突
router eigrp 100
 variance 2

13. 防止外部或特定邻居引入异常大量的路由信息而导致路由器资源枯竭。在 R3 和 R4 上按邻居限制可接收的最大前缀 (Prefix) 数量,若超过限制,设置为产生警告或立即切断 (Shutdown) 该对等关系。
## 需要开启 EIGRP命名模式
router eigrp EIGRP
 address-family ipv4 unicast autonomous-system 100
  maximum-prefix 100

14. R1, R2 应阻止通过连接 PC 的接口泄露 EIGRP Hello 数据包以防拓扑信息外露。此外,在 R1-R4 上禁止动态发现 (Multicast),配置为仅与明确指定的路由器进行单播 (Unicast) 通信。
router eigrp 100
 passive-interface g0/0
 neighbor 100.1.3.3 GigabitEthernet0/1