常考小点配置.note
·无论怎样都要写的:
# 无论题目怎么出都需要写这条规则:
nft add rule ip filter input ct state established,related accept

## 模板:/usr/share/doc/nftables/examples/ct_helpers.nft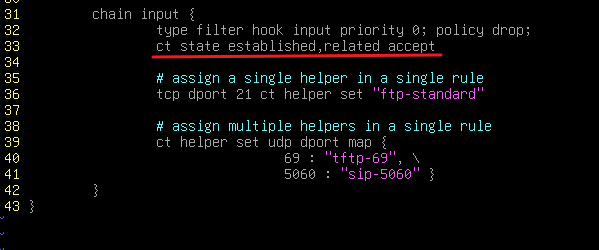
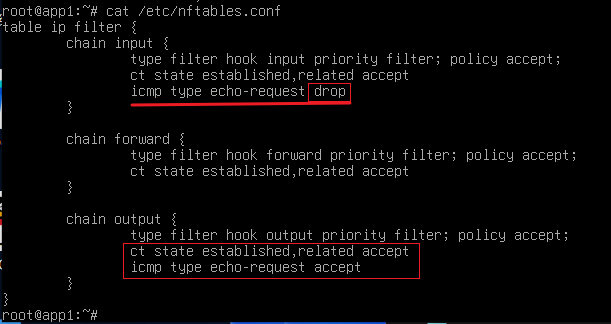
1、允许ping其它任何机器,但是不允许被ping:
如果题目要求 output默认策略是 drop,那么就需要配置放行 icmp type echo-request
nft add rule ip filter output icmp type echo-request accept

cat /etc/nftables.conf
# 需要将input默认策略配置为drop或者在input上配置 icmp type echo-request drop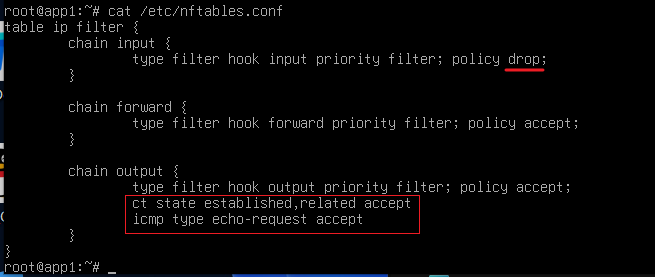
or
2、丢弃无效的数据包:
nft add rule ip filter input ct state invalid drop

cat /etc/nftables.conf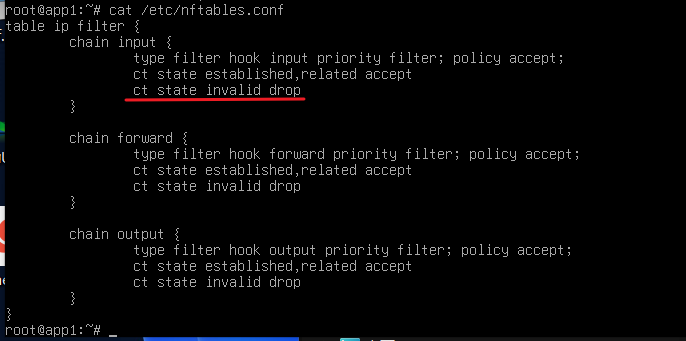
3、ssh 三次输入密码错误就拒绝连接一分钟:
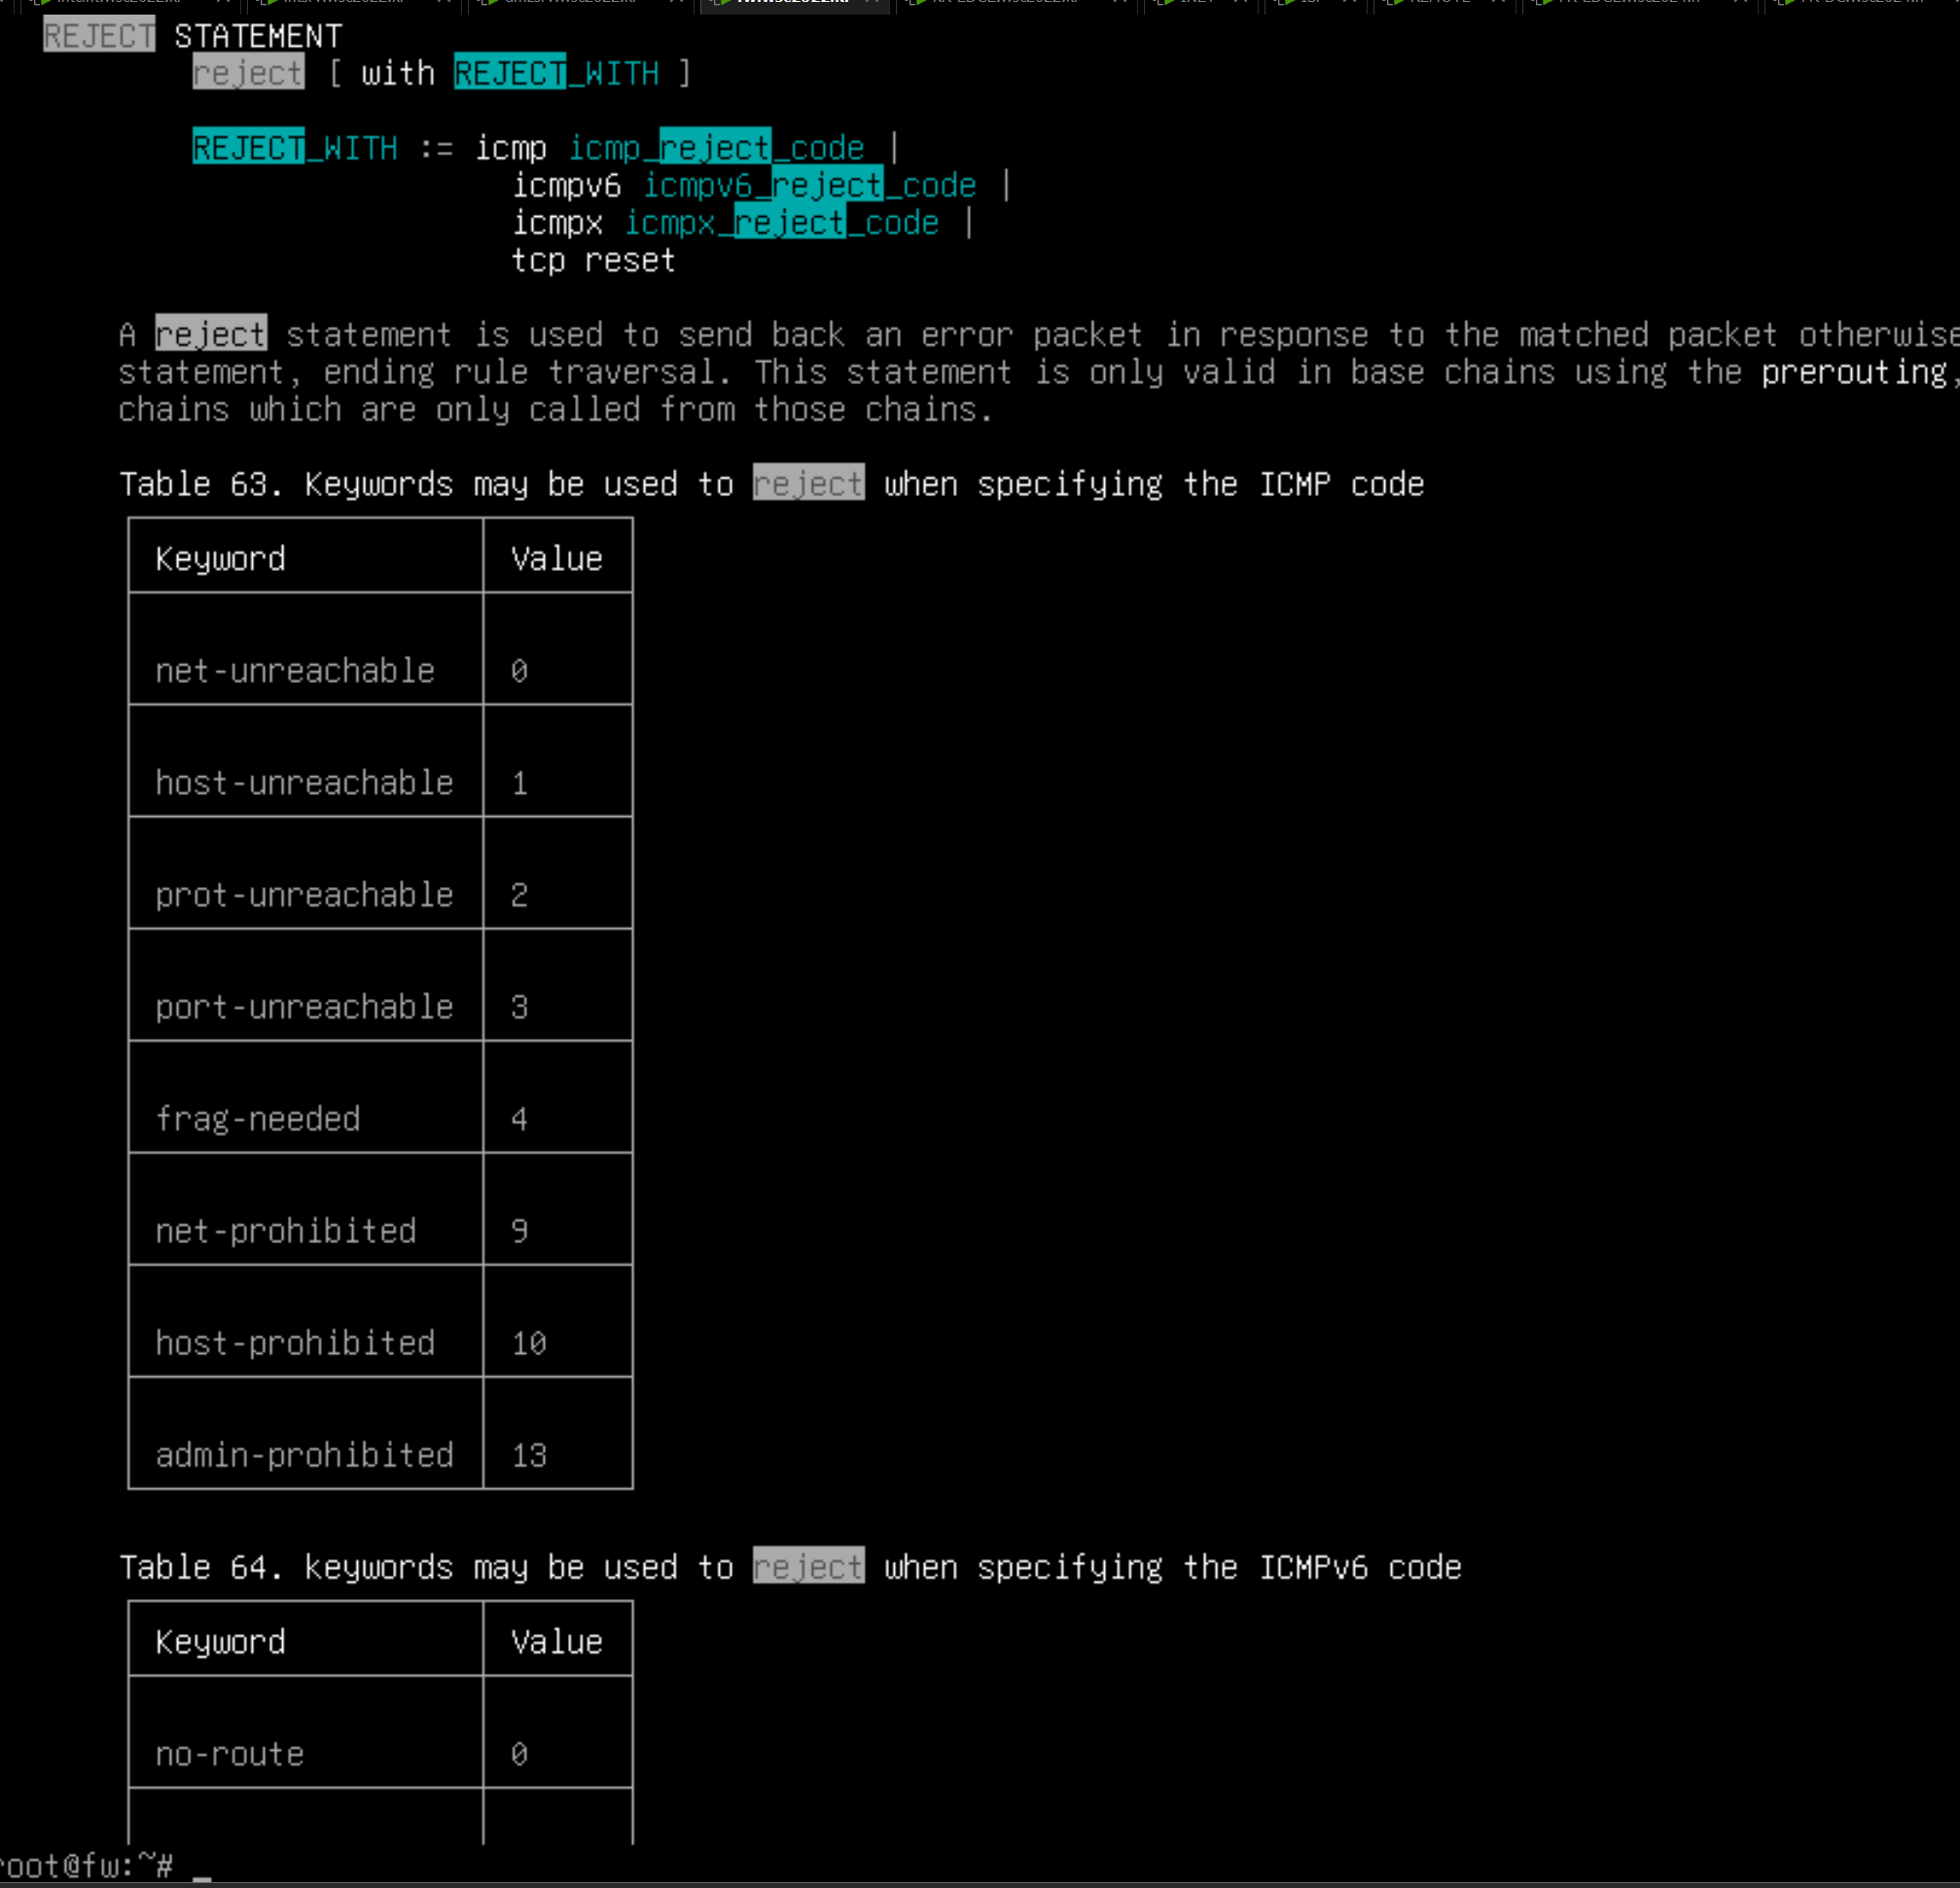
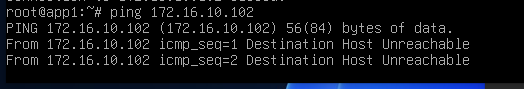
4、拒绝显示主机不可达:
nft add rule ip filter input reject with icmp host-unreachable

cat /etc/nftables.conf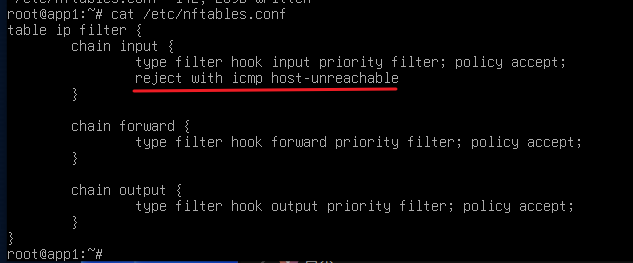
或者可以这样写:
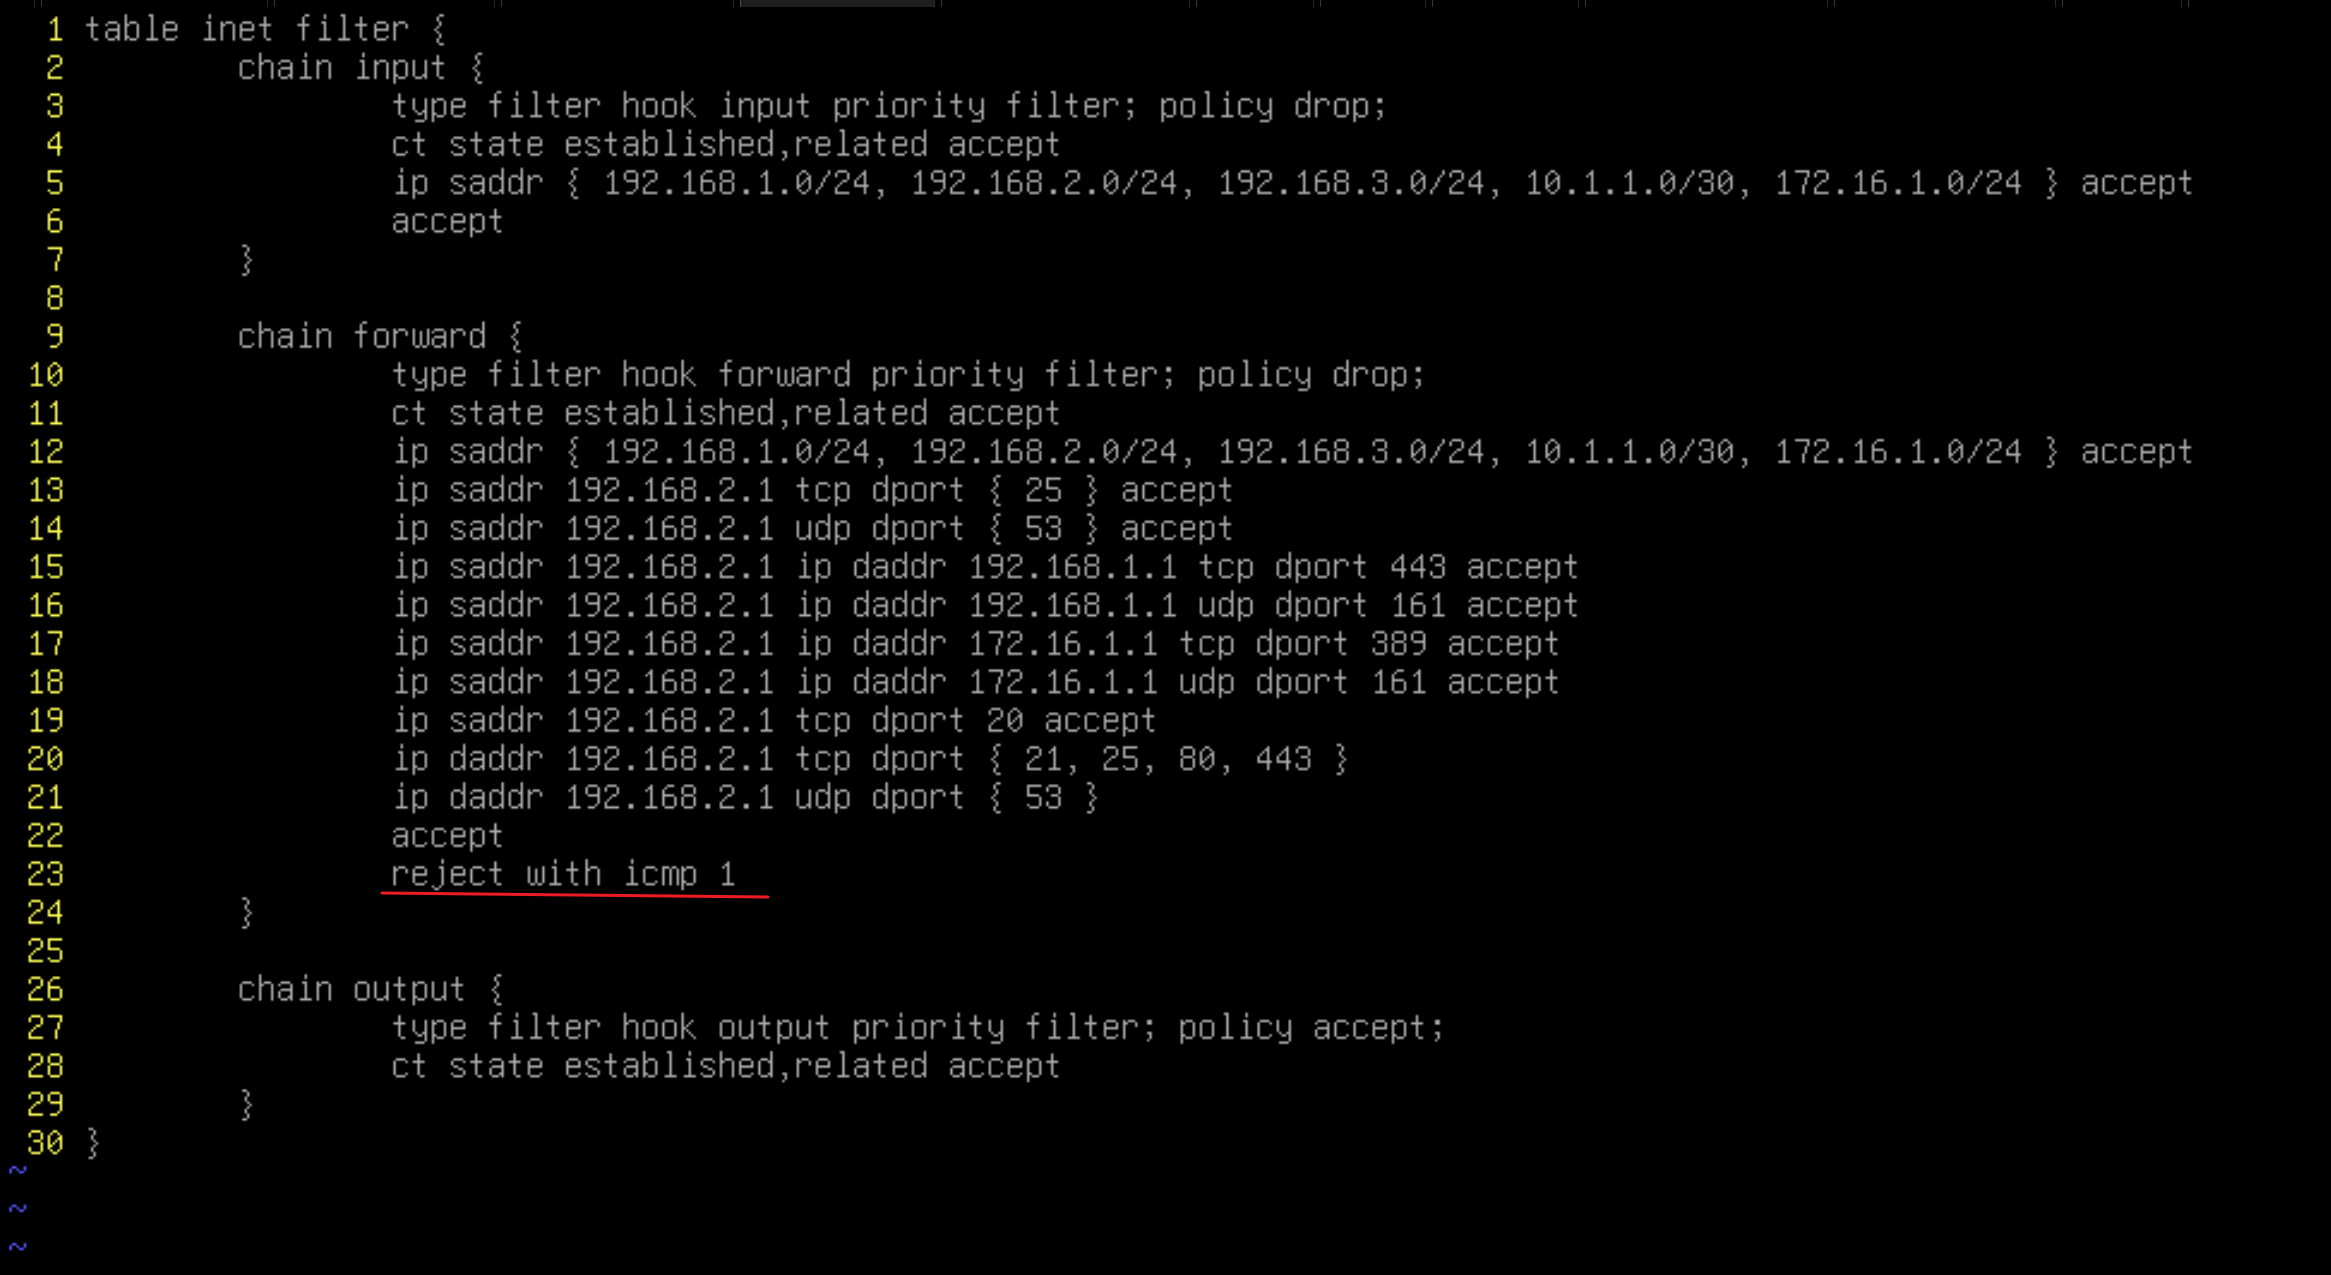
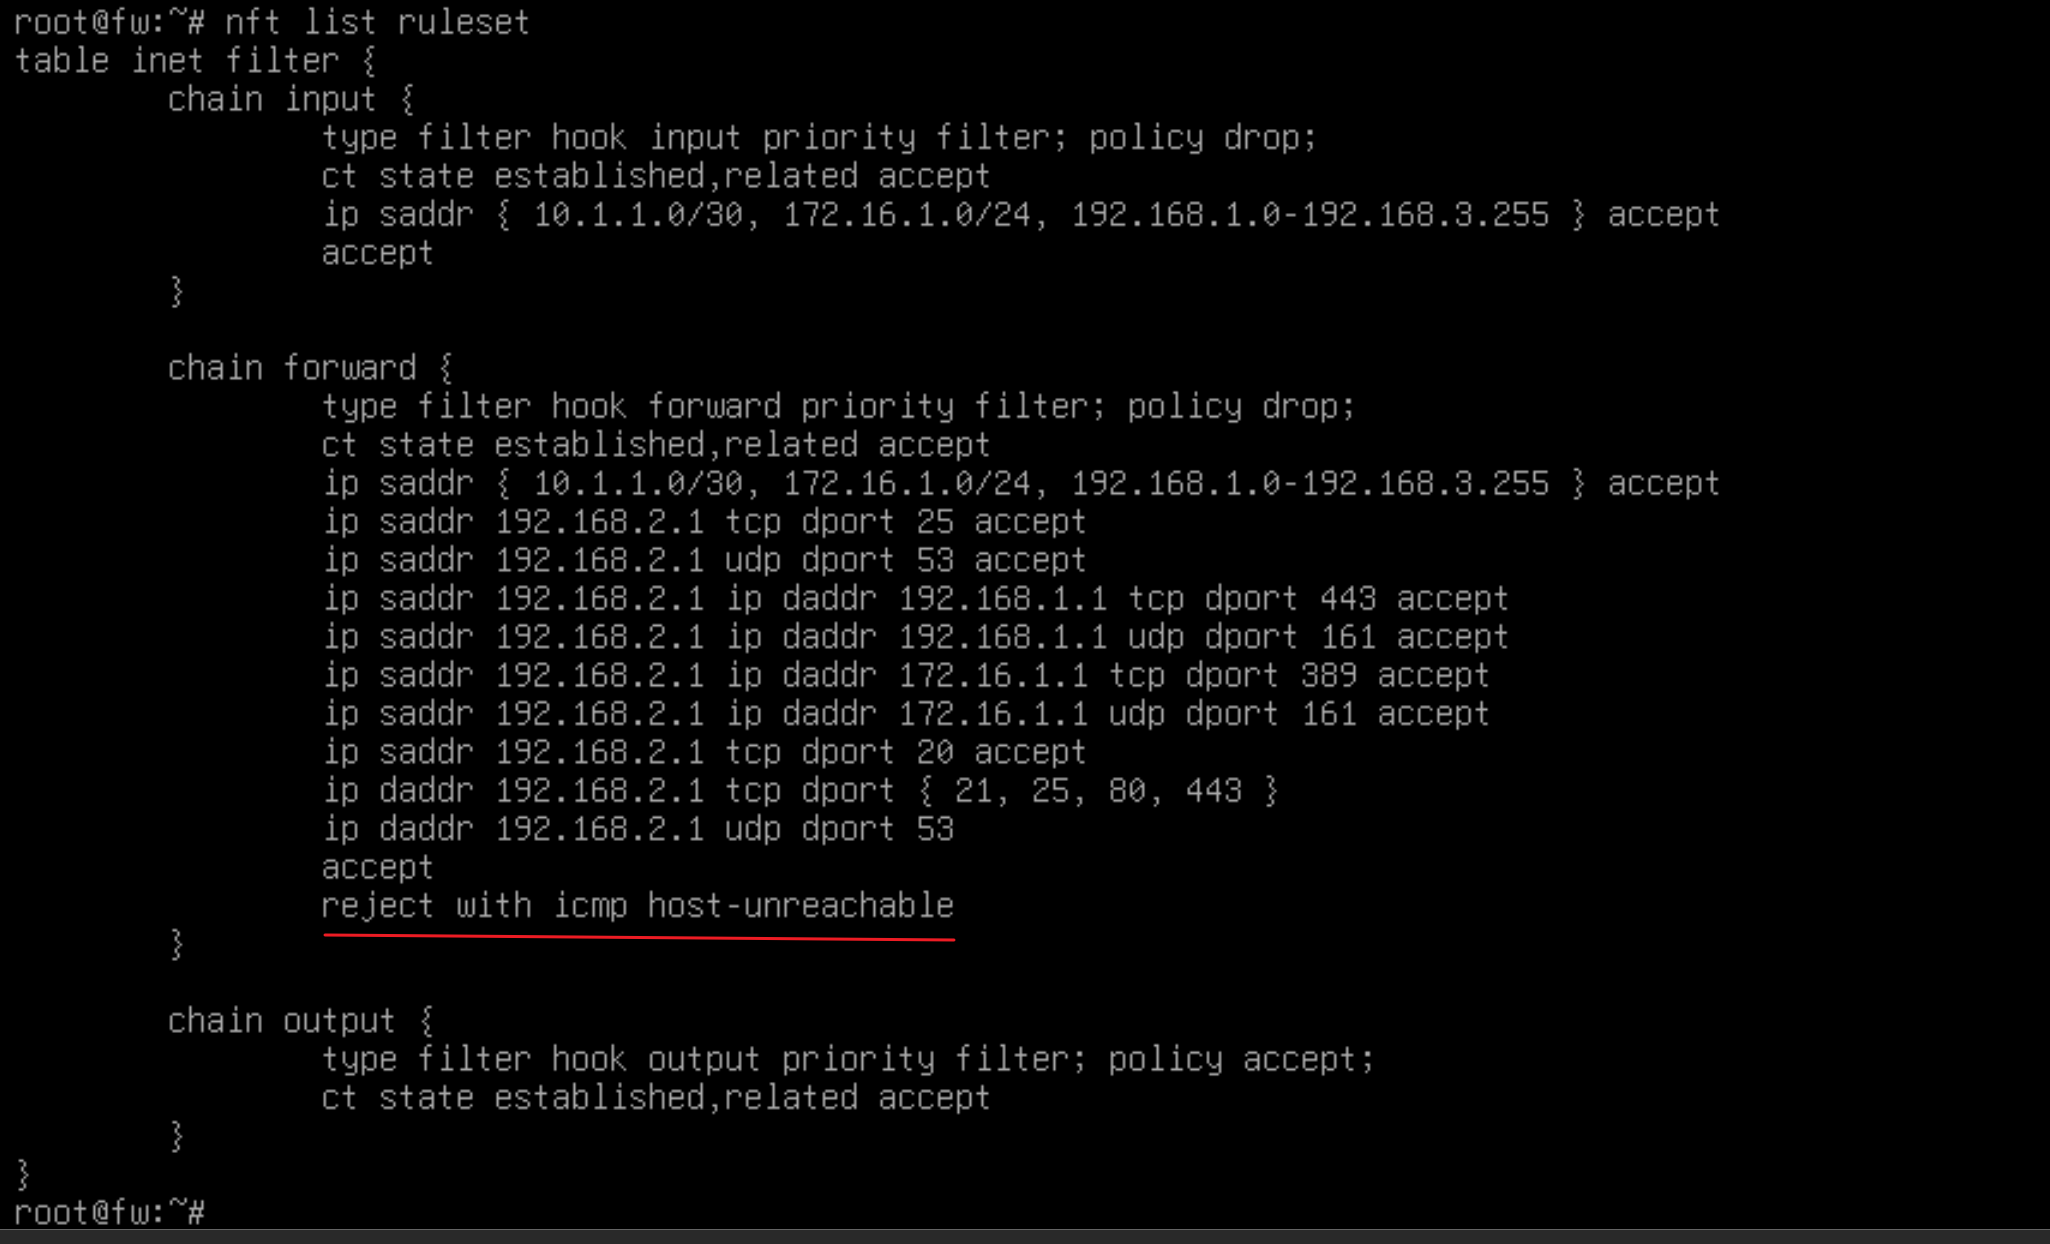
因为在man文档中有定义:
·测试:
5、速率限制:
防火墙速率限制: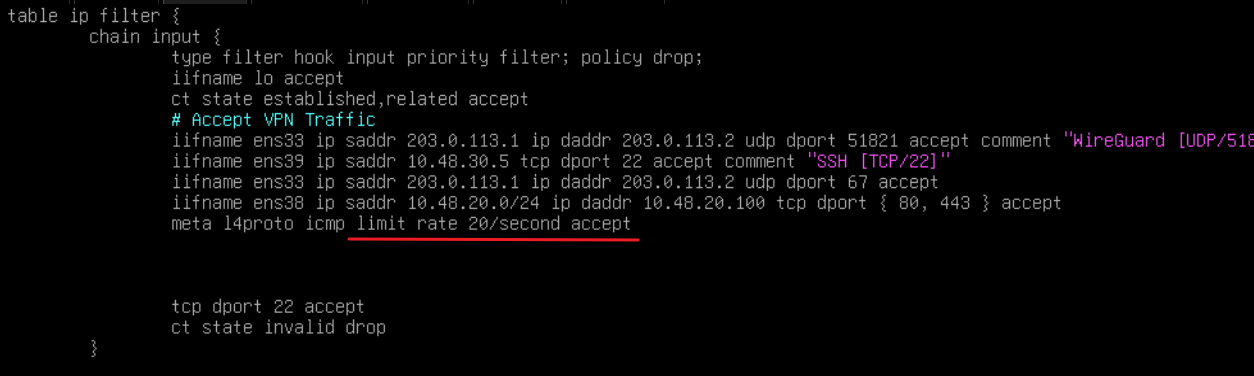
nft list ruleset 中会自动补齐 burst
# 这里的rate表示每秒最多20个包,burst表示允许短时间多5个,也就是一共25个
6、拒绝之后记录日志:
## 记录拒绝日志,日志前缀为:WSC48-SZ-DROP:
# 需要创建一个链,专门用来记录日志,然后将拒绝条目重定向到这个链
vim /etc/nftables.conf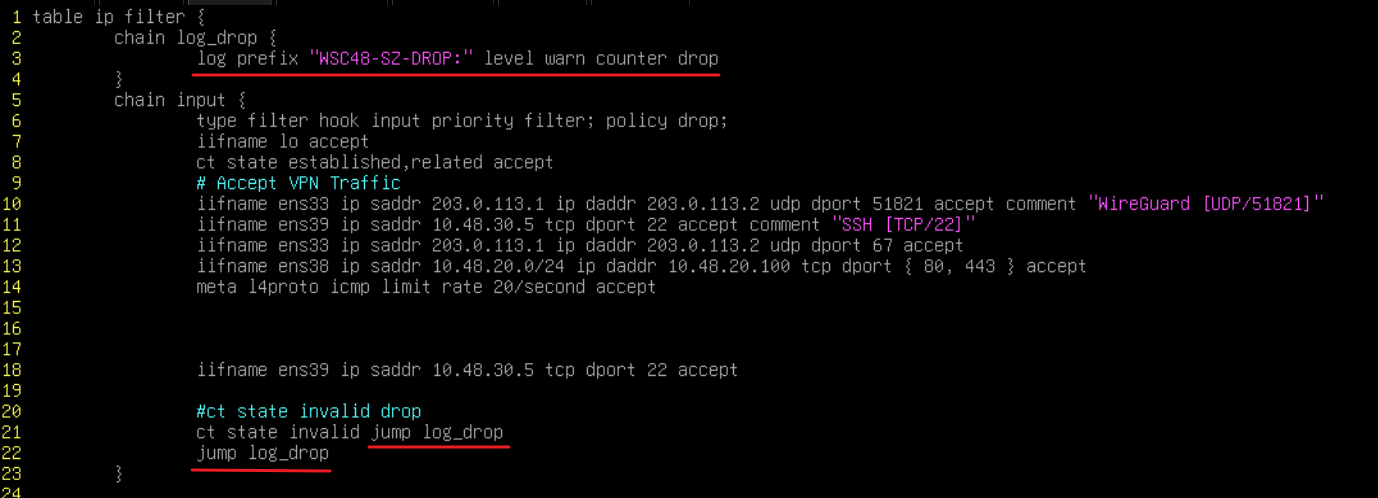
末尾加一条 jump 将所有没有匹配到的条目跳过去
查看:
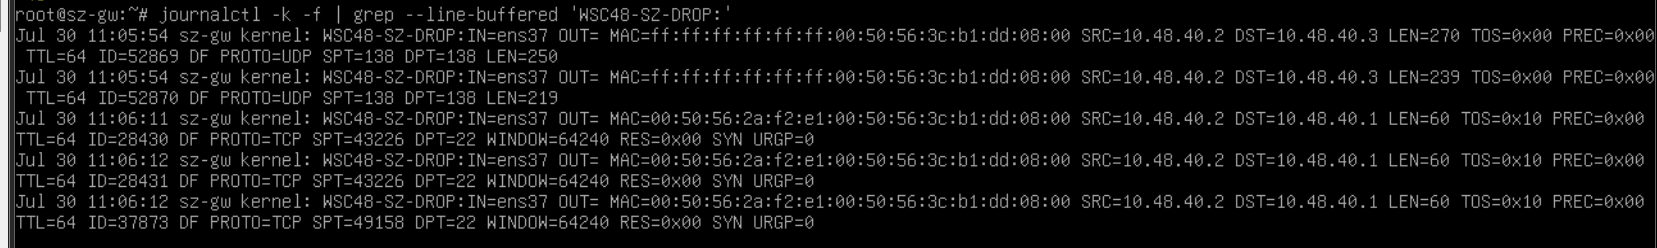
journalctl -k -f | grep --line-buffered 'WSC48-SZ-DROP:'