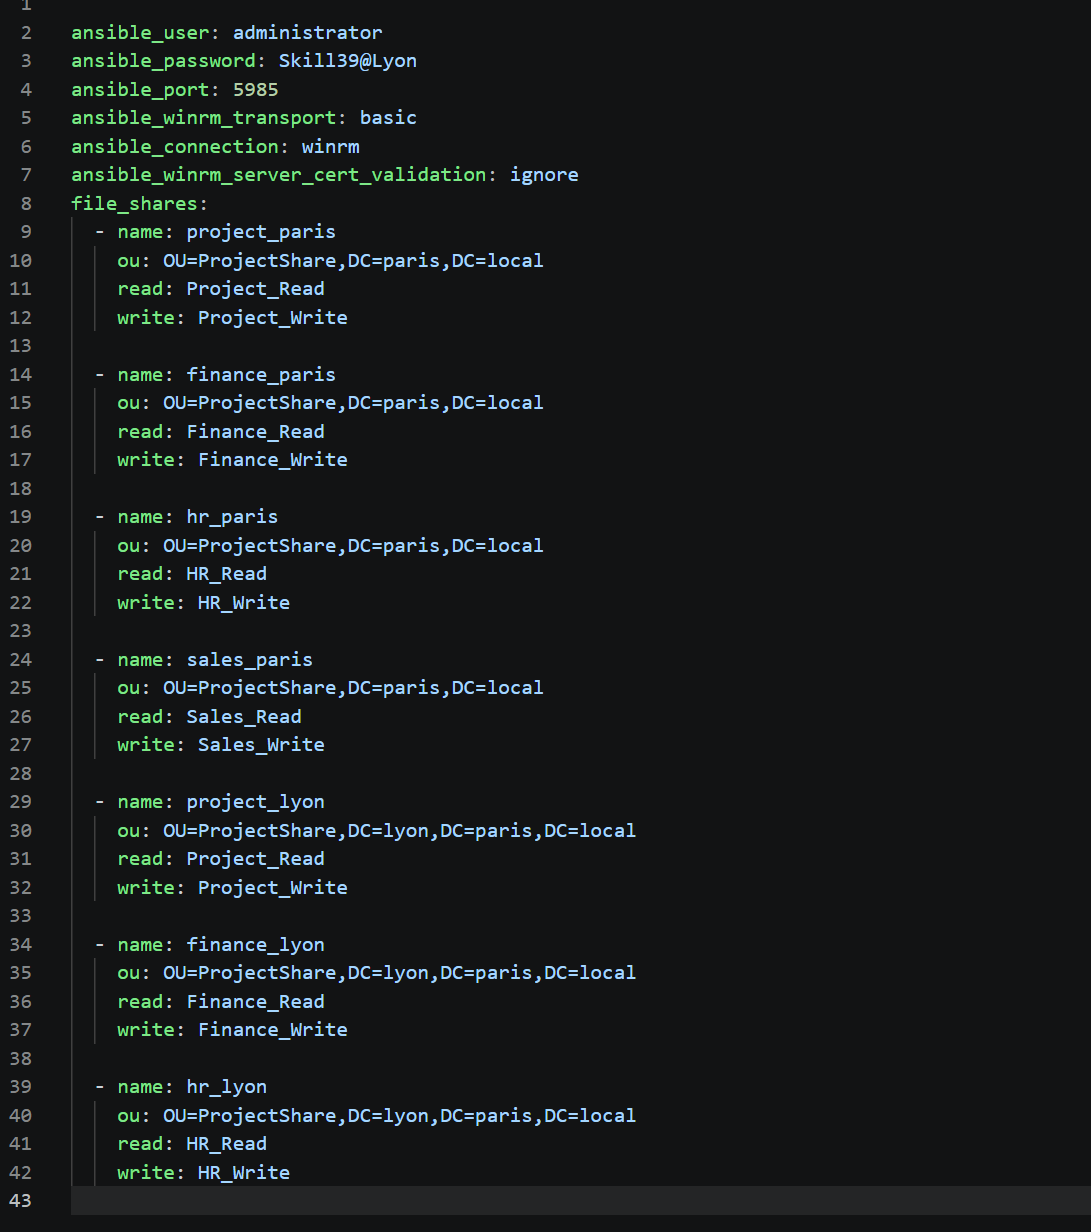
noteId: WEB0810391f1dc4c7d6ec1e63b31ff4fb83 · 原始路径:/ALL/Ansible 自动化管理/Ansible 配置合集/Ansible 自动化管理-Windows/对文件夹、权限的操作/创建文件夹、组,并手动指定 NTFS、共享权限.note · 图片:1 · 附件待处理:2
---
- name: Paris
  hosts: PARIS
  gather_facts: false
  tasks:

    - name: create paris ou
      microsoft.ad.ou:
        name: "{{ item.ou.split(',')[0].split('=')[1] }}"
        domain_server: DC1.paris.local
        domain_username: "PARIS\\Administrator"
        domain_password: "{{ ansible_password }}"
      loop: "{{ file_shares }}"


    - name: create paris read group
      microsoft.ad.group:
        name: "{{ item.read }}"
        path: "{{ item.ou.split(',')[0] }},dc=paris,dc=local"
        scope: global
        domain_server: DC1.paris.local
        domain_username: "PARIS\\Administrator"
        domain_password: "{{ ansible_password }}"
      loop: "{{ file_shares }}"


    - name: create paris write group
      microsoft.ad.group:
        name: "{{ item.write }}"
        path: "{{ item.ou.split(',')[0] }},dc=paris,dc=local"
        scope: global
        domain_server: DC1.paris.local
        domain_username: "PARIS\\Administrator"
        domain_password: "{{ ansible_password }}"
      loop: "{{ file_shares }}"


- name: Lyon
  hosts: LYON
  gather_facts: false
  tasks:
    - name: create Lyon ou
      microsoft.ad.ou:
        name: "{{ item.ou.split(',')[0].split('=')[1] }}"
      loop: "{{ file_shares }}"


    - name: create Lyon Read group
      microsoft.ad.group:
        name: "{{ item.read }}"
        path: "{{ item.ou.split(',')[0] }},dc=lyon,dc=paris,dc=local"
        scope: global
      loop: "{{ file_shares }}"

    - name: create Lyon write group
      microsoft.ad.group:
        name: "{{ item.write }}"
        path: "{{ item.ou.split(',')[0] }},dc=lyon,dc=paris,dc=local"
        scope: global
      loop: "{{ file_shares }}"

- name: Shared the folder
  hosts: all
  gather_facts: false
  tasks:

    - name: create root folder
      win_file:
        path: C:\project_share
        state: directory

    - name: create sub folder
      win_file:
        path: "c:\\project_share\\{{ item.name }}"
        state: directory
      loop: "{{ file_shares }}"


    - name: NTFS disable inheritance
      win_acl_inheritance:
        path: "c:\\project_share\\{{ item.name }}"
        reorganize: false
      loop: "{{ file_shares }}"

    - name: NTFS SYSTEM permission
      win_acl:
        user: SYSTEM
        path: "c:\\project_share\\{{ item.name }}"
        type: allow
        rights: fullcontrol
      loop: "{{ file_shares }}"
      register: file

    - name: NTFS OWNER permission
      win_acl:
        user: CREATOR OWNER
        path: "c:\\project_share\\{{ item.name }}"
        type: allow
        rights: fullcontrol
      loop: "{{ file_shares }}"
      changed_when: file.changed

    - name: NTFS read permission
      win_acl:
        user: "{{ item.read }}"
        path: "c:\\project_share\\{{ item.name }}"
        type: allow
        rights: ReadAndexEcute
      loop: "{{ file_shares }}"

    - name: NTFS write permission
      win_acl:
        user: "{{ item.write }}"
        path: "c:\\project_share\\{{ item.name }}"
        type: allow
        rights: fullcontrol
      loop: "{{ file_shares }}"

    - name: share Folder
      ansible.windows.win_share:
        name: "{{ item.name }}"
        path: "c:\\project_share\\{{ item.name }}"
        full: everyone
      loop: "{{ file_shares }}"