IKEv1 预共享密钥.note
一、点对点建立 隧道:
首先确保公网互通,两端外网 IP能够互通
1、路由器配置:
# 基础IP配置:
int g0/2    // 内网接口
no sh
ip add 192.168.1.254 255.255.255.0

int g0/0    // 外网接口
no sh
ip add 1.1.1.1 255.255.255.0


# 配置 ike协商:
crypto isakmp policy 1

 encr aes 256

 authentication pre-share

 group 14


crypto isakmp key Skills39 address 5.5.5.2     // 配置预共享密钥,指定对端公网地址

# 配置转换集,模式为传输模式:
crypto ipsec transform-set IPSec esp-aes 256 esp-sha-hmac
 mode transport

# 配置 PROFILE:
crypto ipsec profile PROFILE

 set transform-set IPSec

 responder-only    // (可选)安全配置,只响应ike协商,不主动发起ike协商(不能在ASA上配置,ASA配置了会无法建立)

# 配置 tunnel 接口并应用 profile
interface Tunnel0

 ip address 10.0.0.1 255.255.255.252

 tunnel source GigabitEthernet0/0

 tunnel mode ipsec ipv4    // 设置模式为 ipsec ipv4模式(因为ASA防火墙的tunnel只支持这个模式)

 tunnel destination 5.5.5.2

 tunnel protection ipsec profile PROFILE    // 应用 profile

# 配置静态路由,将对端内网地址引入 tunnel 接口:
ip route 172.16.1.0 255.255.255.0 tunnel 0
2、ASA防火墙配置:
# 基础配置:
int g0/0    // 内网接口
 no sh
 nameif inside
 ip add 172.16.1.254 255.255.255.0
 exit

int g0/1    // 外网接口
 no sh
 nameif outside
 ip add 5.5.5.2 255.255.255.0
 exit

same-security-traffic permit inter-interface

same-security-traffic permit intra-interface

access-list ALLOW extended permit ip any any
access-group ALLOW global

policy-map global_policy

 class inspection_default

  inspect icmp


# 配置 ike协商:
crypto ikev1 enable outside
crypto ikev1 policy 1

 authentication pre-share

 encryption aes-256

 hash sha

 group 14

# 配置预共享密钥,并指定对端公网地址:
tunnel-group 1.1.1.1 type ipsec-l2l

tunnel-group 1.1.1.1 ipsec-attributes

 ikev1 pre-shared-key Skills39

# 配置转换集
crypto ipsec ikev1 transform-set IPSec esp-aes-256 esp-sha-hmac

# 配置 profile
crypto ipsec profile PROFILE

 set ikev1 transform-set IPSec

# 配置 tunnel 接口,并应用 profile:
interface Tunnel0

 nameif tunnel    // 必须要有 nameif 才能够应用 profile

 ip address 10.0.0.2 255.255.255.252

 tunnel source interface outside

 tunnel destination 1.1.1.1    // 对端外网地址

 tunnel mode ipsec ipv4

 tunnel protection ipsec profile PROFILE    // 应用 profile

# 配置静态路由,将对端内网地址引入 tunnel 接口:
route tunnel 192.168.1.0 255.255.255.0 10.0.0.1
二、点对多点建立隧道:
类似这样的拓扑:
EDGERTR有两个出接口通往 EDGEFW
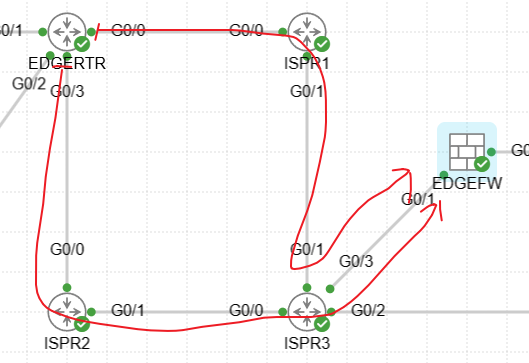
使用 EDGERTR的 Loopback 接口建立即可
不用看下面的配置,下面的配置对不上(是在ASA上建立两个tunnel接口来连接的配置)
首先确保公网互通,两端外网 IP能够互通
1、路由器配置:
# 基础IP配置:
int g0/2    // 内网接口
no sh
ip add 192.168.1.254 255.255.255.0

int g0/0    // 外网接口1
no sh
ip add 1.1.1.1 255.255.255.0

int g0/3    // 外网接口2
no sh
ip add 2.2.2.1 255.255.255.0


crypto isakmp policy 1

 encr aes 256

 authentication pre-share

 group 14


crypto isakmp key Skills39 address 5.5.5.2     // 配置预共享密钥,指定对端公网地址

crypto ipsec transform-set IPSec esp-aes 256 esp-sha-hmac
 mode transport

crypto ipsec profile PROFILE

 set transform-set IPSec

 responder-only    // (可选)安全配置,只响应ike协商,不主动发起ike协商(不能在ASA上配置,ASA配置了会无法建立)

interface Tunnel0

 ip address 10.0.0.1 255.255.255.252

 tunnel source GigabitEthernet0/0

 tunnel mode ipsec ipv4    // 设置模式为 ipsec ipv4模式(因为ASA防火墙的tunnel只支持这个模式)

 tunnel destination 5.5.5.2

 tunnel protection ipsec profile PROFILE    // 应用 profile

ip route 172.16.1.0 255.255.255.0 tunnel 0

# 新增配置:
int tunn 1
 no sh
 ip add 11.0.0.1 255.255.255.0
 tunnel source GigabitEthernet0/3
 tunnel destination 5.5.5.2
 tunnel mode ipsec ipv4
 tunnel protection ipsec profile PROFILE

ip route 172.16.1.0 255.255.255.0 tunnel 1
2、ASA防火墙配置:
int g0/0    // 内网接口
 no sh
 nameif inside
 ip add 172.16.1.254 255.255.255.0
 exit

int g0/1    // 外网接口
 no sh
 nameif outside
 ip add 5.5.5.2 255.255.255.0
 exit

same-security-traffic permit inter-interface

same-security-traffic permit intra-interface

access-list ALLOW extended permit ip any any
access-group ALLOW global

policy-map global_policy

 class inspection_default

  inspect icmp


crypto ikev1 enable outside
crypto ikev1 policy 1

 authentication pre-share

 encryption aes-256

 hash sha

 group 14

tunnel-group 1.1.1.1 type ipsec-l2l

tunnel-group 1.1.1.1 ipsec-attributes

 ikev1 pre-shared-key Skills39

crypto ipsec ikev1 transform-set IPSec esp-aes-256 esp-sha-hmac

crypto ipsec profile PROFILE

 set ikev1 transform-set IPSec

interface Tunnel0

 nameif tunnel    // 必须要有 nameif 才能够应用 profile

 ip address 10.0.0.2 255.255.255.252

 tunnel source interface outside

 tunnel destination 1.1.1.1    // 对端外网地址

 tunnel mode ipsec ipv4

 tunnel protection ipsec profile PROFILE    // 应用 profile

route tunnel 192.168.1.0 255.255.255.0 10.0.0.1


# 新增的配置:
tunnel-group 2.2.2.1 type ipsec-l2l
tunnel-group 2.2.2.1 ipsec-attributes
 ikev1 pre-shared-key Skills39

int tunnel 1
 nameif tunnel1
 ip add 11.0.0.2 255.255.255.0
 tunnel source interface outside
 tunnel destination 2.2.2.1
 tunnel mode ipsec ipv4
 tunnel protection ipsec profile PROFILE

route tunnel1 192.168.1.0 255.255.255.0 11.0.0.1 2    // ASA不能够配置等价负载均衡的路由(ASA防火墙不支持),只能够配置浮动路由了