路由.note
7、接口带宽、mtu、延迟:
## BR-GW-RTR-01:
int ra g0/5-6
 mtu 1400
 bandwidth 500000
 delay 100

## HQ-GW-RTR-01:
int ra g0/5
 mtu 1400
 bandwidth 500000
 delay 100

## HQ-GW-RTR-02:
int ra g0/6
 mtu 1400
 bandwidth 500000
 delay 100
8、静态默认路由:
# RTR01:
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/1 155.155.128.217
# RTR02:
ip route 0.0.0.0 0.0.0.0 GigabitEthernet0/1 169.138.115.138
9、eigrp、重分发vlan、默认路由:
通告内网接口(g0/2、3、4),与BR-GW连接的接口不通告
不需要通告 Loopback接口
## HQ-GW-RTR-01:
router eigrp 2023
 eigrp router-id 10.0.0.1
 network 172.16.10.0 0.0.0.3
 network 172.16.13.0 0.0.0.3
 network 172.16.13.4 0.0.0.3
 redistribute static    //重分发默认路由时不要指定metric

## HQ-GW-RTR-02:
router eigrp 2030
 eigrp router-id 10.0.0.2
 network 172.16.10.0 0.0.0.3
 network 172.16.13.8 0.0.0.3
 network 172.16.13.12 0.0.0.3
 redistribute static    //重分发默认路由时不要指定metric

## NOC-COR-SW-01:
### 重分发vlan 10、20:
route-map VLAN
 match interface Vlan10 vlan20

router eigrp 2030
 eigrp router-id 10.0.0.11
 network 172.16.13.0 0.0.0.3
 network 172.16.13.12 0.0.0.3
 network 172.16.13.252 0.0.0.3
 redistribute connected route-map VLAN    //重分发直连路由时不要指定metric

## NOC-COR-SW-02:
### 重分发vlan 10、20:
route-map VLAN
 match interface Vlan10 vlan20

router eigrp 2030
 eigrp router-id 10.0.0.12
 network 172.16.13.4 0.0.0.3
 network 172.16.13.8 0.0.0.3
 network 172.16.13.252 0.0.0.3
 redistribute connected route-map VLAN    //重分发直连路由时不要指定metric
10、ospf、点对点链路:
· RTR-01、RTR-02、BR之间的链路要修改 mtu、带宽、延迟(只修改一边会导致不通):
int g0/5
 mtu 1400
 bandwidth 500000
 delay 100
# HQ-GW-RTR-01:
router ospf 2030
router-id 10.0.0.1
network 172.16.11.4 0.0.0.3 area 0
int g0/5
ip ospf network point-to-point
# HQ-GW-RTR-02:
router ospf 2030
router-id 10.0.0.2
network 172.16.12.4 0.0.0.3 area 0
int g0/6
ip ospf network point-to-point
# BR-GW-RTR-01:
## 重分发直连(包括Loopback接口):
route-map CONNECT
match interface G0/2 Loopback0 g0/2.10 g0/2.99
router ospf 2030
router-id 10.0.0.3
network 172.16.11.4 0.0.0.3 area 0
network 172.16.12.4 0.0.0.3 area 0
redistribute connected metric 2030 subnets tag 2030 route-map CONNECT
int ra g0/5-6
ip ospf network point-to-point
ip ospf network point-to-point11、eigrp、ospf 双点双向重分发:
带宽、延迟、mtu 等参数就和上面设置的一样
这里的双点双向重分发暂时不需要将eigrp 外部AD值降低(应该?)
route-map TO-OSPF deny 10
 match tag 2031
route-map TO-OSPF permit 20
 set tag 2032

route-map TO-EIGRP deny 10
 match tag 2032
route-map TO-EIGRP permit 20
 set tag 2031

# RTR-01:
router eigrp 2030
 redistribute ospf 2030 metric 500000 100 255 1 1400 route-map TO-EIGRP

router ospf 2030
 redistribute eigrp 2030 metric-type 1 subnets route-map TO-OSPF

# RTR-02:
router eigrp 2030
 redistribute ospf 2030 metric 500000 100 255 1 1400 route-map TO-EIGRP

router ospf 2030
 redistribute eigrp 2030 metric-type 1 subnets route-map TO-OSPF
·路由汇总:
# BR-RTR01:
router ospf 2030
 summary-address 10.1.0.0 255.255.128.0

# NOC-SW-01:
int ra g0/1-2
  ip summary-address eigrp 2030 172.16.128.0 255.255.128.0
# NOC-SW-02:
int ra g0/1-2
  ip summary-address eigrp 2030 172.16.128.0 255.255.128.0
12、公网ospf路由:
·整体拓扑:
## ospf 进程仅本地有效,建立邻居实际上还是看area区域号
1、SH-EDGE-ISP-01、DJ-EDGE-ISP-01 和 IDS-FW 之间用 area 0 相连建立邻居
2、SH-WAN-RTR-01、DJ-WAN-CORE-RTR-01 和 IDS-FW 之间用 area 1 相连建立邻居(因为IDS-FW上有area 0,所以不会出问题)
3、RW-WAN-CORE-RT01 和 DJ-WAN-CORE-RTR-01 之间用 area 2 相连建立邻居,因为此时没有直连到 area 0,所以就需要在 DJ-WAN-CORE-RTR-01 和 IDS-FW做 虚链路
1)进程2027:
通告它们的 Loop0、G3、G4接口,也就是它们的直连接口(G3接口是通过交换机直连的)
# SH-EDGE-ISP-01:
router ospf 2027
 router-id 1.1.1.1
 network 1.1.1.1 0.0.0.0 area 0
 network 102.88.99.248 0.0.0.3 area 0
 network 107.45.128.208 0.0.0.7 area 0

# DJ-EDGE-ISP-01:
router ospf 2027
 router-id 1.1.1.2
 network 1.1.1.2 0.0.0.0 area 0
 network 102.88.99.248 0.0.0.3 area 0
 network 107.45.128.208 0.0.0.7 area 0

# SH、DJ 点对点链路:
int g4
 ip ospf network point-to-point
2)进程2028:
# IDS-FW:
router ospf 2028
 router-id 1.1.252.253
 network 1.1.252.253 255.255.255.255 area 0
 network 107.45.128.208 255.255.255.248 area 0
 network 179.115.134.0 255.255.255.248 area 1
3)进程2029:
# SH-WAN-RTR-01(area 1):
## 发布HQ区域的直连接口(类型1、tag 100):
route-map HQ
 match interface g0/2 g0/3

router ospf 2029
 router-id 1.1.1.10
 redistribute connected subnets metric-type 1 tag 100 route-map HQ
 network 1.1.1.10 0.0.0.0 area 1
 network 179.115.134.0 0.0.0.7 area 1

# DJ-WAN-CORE-RTR-01(area 1):
router ospf 2029
 router-id 1.1.1.11
 network 1.1.1.11 0.0.0.0 area 1
 network 179.115.134.0 0.0.0.7 area 1
 network 219.158.195.192 0.0.0.15 area 2

int g0/2
 ip ospf network point-to-point

# RW-WAN-CORE-RT01(area 2):
## 发布BR区域的直连接口(类型1、tag 200):
route-map BR permit 10
 match interface BVI1

router ospf 2029
 router-id 1.1.1.12
 network 1.1.1.12 0.0.0.0 area 2
 network 219.158.195.192 0.0.0.15 area 2
 redistribute connected subnets metric-type 1 tag 200 route-map BR

int g0/1
 ip ospf network point-to-point
4)虚链路:
# IDS-FW:
router ospf 2028
 area 1 virtual-link 1.1.1.11
# DJ-WAN-CORE-RTR-01:
router ospf 2029
 area 1 virtual-link 1.1.252.253
5)totally nssa:
必须要配置了虚链路,成功连接上 area 0才会获取到下发的默认路由
# DJ-WAN-CORE-RTR-01:
router ospf 2029
 area 2 nssa default-information-originate no-summary

# RW-WAN-CORE-RT01:
router ospf 2029
 area 2 nssa
13、ASA 配置:
# 放行相同安全等级的流量:
same-security-traffic permit inter-interface
# 开启 TTL显示:
show run policy-map
policy-map global_policy
class class-default
set connection decrement-ttl14、公网 BGP:
只需要键 eBGP邻居,不需要建 iBGP
·EXT-ISP-GW 上配置 Null 默认路由:
ip route 0.0.0.0 0.0.0.0 Null 0注意,该路由需要通告,而不是重分发
1)基础配置:
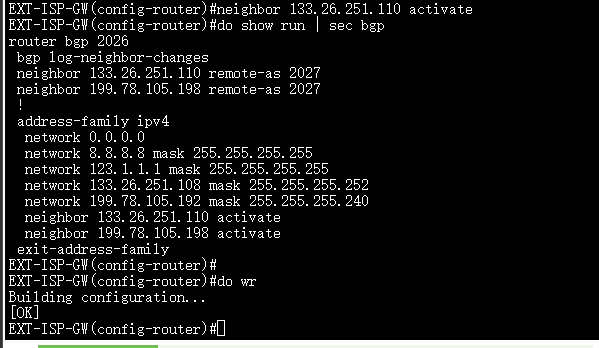
# EXT-ISP-GW:
router bgp 2026
 neighbor 133.26.251.110 remote-as 2027
 neighbor 199.78.105.198 remote-as 2027

 network 0.0.0.0
 network 8.8.8.8 mask 255.255.255.255
 network 123.1.1.1 mask 255.255.255.255
 network 133.26.251.108 mask 255.255.255.252
 network 199.78.105.192 mask 255.255.255.240
按照这个配置之后,直接加个 activate,就会自动转换为 ipv4 的地址簇:
# SH-EDGE-ISP-01:
router bgp 2027
 neighbor 1.1.1.2 remote-as 2027
 neighbor 1.1.1.2 update-source Loopback0
 neighbor 107.45.128.214 remote-as 2028
 neighbor 133.26.251.109 remote-as 2026
 !
 address-family ipv4
  network 88.134.135.0 mask 255.255.255.248
  network 133.26.251.108 mask 255.255.255.252
  network 188.135.134.0 mask 255.255.255.248
  neighbor 1.1.1.2 activate
  neighbor 1.1.1.2 next-hop-self
  neighbor 107.45.128.214 activate
  neighbor 133.26.251.109 activate
# DJ-EDGE-ISP-01:
router bgp 2027
neighbor 1.1.1.1 remote-as 2027
neighbor 1.1.1.1 update-source Loopback0
neighbor 107.45.128.214 remote-as 2028
neighbor 199.78.105.204 remote-as 2026
!
address-family ipv4
network 99.134.135.0 mask 255.255.255.248
network 199.78.105.192 mask 255.255.255.240
network 199.135.134.0 mask 255.255.255.248
redistribute ospf 2027 match internal external 1 external 2 route-map BGP_OSPF
neighbor 1.1.1.1 activate
neighbor 1.1.1.1 next-hop-self
neighbor 107.45.128.214 activate
neighbor 199.78.105.204 activate
exit-address-family# IDS-FW:
router bgp 2028
address-family ipv4 unicast
neighbor 179.115.134.5 remote-as 2029
neighbor 179.115.134.5 activate
neighbor 179.115.134.6 remote-as 2029
neighbor 179.115.134.6 activate
neighbor 107.45.128.209 remote-as 2027
neighbor 107.45.128.209 activate
neighbor 107.45.128.210 remote-as 2027
neighbor 107.45.128.210 activate
exit-address-family# SH-WAN-RTR-01:
router bgp 2029
neighbor 1.1.1.11 remote-as 2029
neighbor 1.1.1.11 update-source Loopback0
neighbor 179.115.134.1 remote-as 2028
!
address-family ipv4
network 34.197.88.16 mask 255.255.255.240
network 88.134.135.0 mask 255.255.255.248
network 199.135.134.0 mask 255.255.255.248
neighbor 1.1.1.11 activate
neighbor 1.1.1.11 next-hop-self
neighbor 179.115.134.1 activate
exit-address-family# DJ-WAN-CORE-RT01:
router bgp 2029
neighbor 1.1.1.10 remote-as 2029
neighbor 1.1.1.10 update-source Loopback0
neighbor 1.1.1.12 remote-as 2029
neighbor 1.1.1.12 update-source Loopback0
neighbor 179.115.134.1 remote-as 2028
!
address-family ipv4
network 99.134.135.0 mask 255.255.255.248
network 188.135.134.0 mask 255.255.255.248
neighbor 1.1.1.10 activate
neighbor 1.1.1.10 route-reflector-client
neighbor 1.1.1.10 next-hop-self
neighbor 1.1.1.12 activate
neighbor 1.1.1.12 route-reflector-client
neighbor 1.1.1.12 next-hop-self
neighbor 179.115.134.1 activate
exit-address-family# RW-WAN-CORE-RTR01:
router bgp 2029
bgp log-neighbor-changes
neighbor 1.1.1.11 remote-as 2029
neighbor 1.1.1.11 update-source Loopback0
!
address-family ipv4
network 23.186.54.112 mask 255.255.255.240
network 52.118.233.176 mask 255.255.255.240
network 64.171.92.144 mask 255.255.255.240
network 98.143.201.160 mask 255.255.255.240
network 116.35.240.48 mask 255.255.255.240
network 145.72.199.32 mask 255.255.255.240
network 173.44.67.16 mask 255.255.255.240
network 187.209.14.96 mask 255.255.255.240
network 199.82.156.160 mask 255.255.255.240
network 210.91.8.64 mask 255.255.255.240
neighbor 1.1.1.11 activate
exit-address-family2)配置 bgp反射器:
# DJ-WAN-CORE-RT01:
router bgp 2029
 address-family ipv4
  neighbor 1.1.1.10 route-reflector-client
  neighbor 1.1.1.12 route-reflector-client
·重分发 OSPF:
ospf只需要发送给 ISP,不需要发送给其他机器
#只需要重分发给 iBGP和 EXT-ISP-GW:
## SH-EDGE-ISP-01、DJ-EDGE-ISP-01:
route-map BGP_OSPF
 set community 2026:2026

ip community-list 1 permit 2026:2026
route-map BGP_DENY deny 10
 match community 1
route-map BGP_DENY permit 20

# SH、DJ:
router bgp 2027
 redistribute ospf 2027 match internal external 1 external 2 route-map BGP_OSPF
 neighbor 107.45.128.214 route-map BGP_DENY out
 neighbor 1.1.1.1\2 route-map BGP_DENY out
·路径控制:
# 在IDS-FW上,去往ISP的路由,需要优先通过 SH-EDGE-ISP-01:
## IDS-FW:
route-map BGP1 permit 10
 set local-preference 100

router bgp 2028
 address-family ipv4 unicast
  neighbor 107.45.128.210 route-map BGP1 in
15、隧道 OSPF:
要先配置完 IKEv2 隧道才能配置
# EXT-ISP-GW:
router ospf 4839
 router-id 111.111.222.1
 network 111.111.222.0 255.255.255.252 area 0

int tunn 0
 ip mtu 1422    //根据对端ASA的tunnel地址设置

# IDS-FW:
router ospf 4839
 router-id 111.111.222.2
 network 111.111.222.0 255.255.255.252 area 0
 network 111.111.111.0 255.255.255.0 area 1


# HQ-GW-RTR-02:
router ospf 4839
 router-id 111.111.111.101
 network 111.111.111.0 0.0.0.255 area 1

# BR-GW-RTR-01:
router ospf 4839
 router-id 111.111.111.102
 network 111.111.111.0 0.0.0.255 area 1
16、策略路由:
确保 HQ-RTR-01、02 上为 BR的内网配置了NAT,配置了连接br的接口为 ip nat inside
# BR-GW-RTR-01:
ip sla 1
 icmp-echo 172.16.11.5 source-interface GigabitEthernet0/6
 frequency 5
ip sla schedule 1 life forever start-time now
ip sla 2
 icmp-echo 172.16.12.6 source-interface GigabitEthernet0/5
 frequency 5
ip sla schedule 2 life forever start-time now
track 1 ip sla 1 reachability
track 2 ip sla 2 reachability

route-map PBR permit 10
 match ip address 1
 set ip next-hop verify-availability 172.16.11.5 1 track 1
 set ip next-hop verify-availability 172.16.12.6 2 track 2

interface GigabitEthernet0/2.10
 ip policy route-map PBR