注意事项、交换.note
·注意事项:
·比赛开始前,先将 LAB-MGT-SW1 关掉,防止交换机环路

如果有时候ping不通 vlan地址、vrrp地址,需要手动重启一下vlan

1、交换:不要做lacp热备份,和native tag,会出问题(做了lacp热备会导致eigrp 一端反复up、down,另一端没有邻居状态)
(native vlan可以写在banner中)

2、要修改MTU和延迟时,必须两端同时修改,并且eigrp重分发时也要使用这个新的mtu和延迟

3、题目没有给定交换机vlan的地址,可以自定义,我这里用的是(注意Vlan20必须有一个是.254(vrrp主设备那台)):
# COR-SW1:
vlan10:172.16.191.253/24
vlan20:172.16.200.253/24
# COR-SW2:
vlan10:172.16.191.252/24
vlan20:172.16.200.254/24
# ACC-SW1:
vlan20:172.16.200.201/24
# ACC-SW2:
vlan20:172.16.200.202/24

4、hsrp、vrrp 的track,要track4条链路(注意:vrrp主设备不能配置 track,否则会出问题,track配置在另一端即可;COR-SW01设备的vlan20 IP 必须配置为 172.16.200.254,这样它的优先级才会成为 255,并且配置中也不能够手动使用pri指定优先级)

5、eigrp 重分发,最好用改过的那个带宽和延迟、MTU:redi conn metric 500000 100 255 1 1400

6、内网路由(eigrp、ospf):只需要宣告直连内网网段,不需要宣告 loopback接口

7、公网路由(ospf):需要宣告区域直连网段 和 loopbakcup接口

8、公网OSPF,DJ-WAN-CORE-RT01 和 IDS-FW之间要配置虚链路,否则RW-WAN-CORE-RT01 的OSPF会出问题(并且nssa的默认路由也需要在连接到骨干区域后才会下发)。

9、公网BGP,题目说了,要使用 IPv4 地址簇,可以正常配置,配置完后可以使用 activate 让它自动转换

10、公网BGP,要对iBGP邻居配置 next-hop-self(需要配置的设备:SH-EDGE-ISP-01、DJ-EDGE-ISP-01、SH-WAN-RTR-01、DJ-WAN-RTR-01)

11、公网BGP,DJ-WAN-CORE-RT01上要配置反射器(反射器客户端:SH-WAN-RTR-01、RW-WAN-CORE-RT01)

12、记得给 ACC交换机配置地址,默认路由,让他们能够访问ISP进行时间同步(包括ACC-03)

13、记得给 BR区域客户端配置 ipv6地址,静态也行、slaac也行,有地址就行

14、HQ-RTR01、RTR02 有一台会NTP同步失败,能ping通但是同步不上,需要将源设置为内网接口地址(ntp server 8.8.8.8 source GigabitEthernet0/3)

15、acc-03上,要为 trunk 接口配置 portfast

16、acc-03上,要将natvie vlan 设置为 99;并且要关闭 DTP(sw no)

17、eigrp 在HQ-RTR上重分发默认路由时不需要指定metric值;在COR-SW交换机上重分发直连(VLAN接口时)不需要指定 metric值;只需要在 双点双向重分发,引入 ospf路由时才需要指定metric值(并且值为 接口mtu、带宽、延迟:100000 100 255 1 1400)(只有在涉及修改过带宽的那个链路的路由,才需要指定metric值)

18、路由汇总:第一条:(br区域汇总成: 10.1.0.0/16);第二条:(HQ区域,三层交换机上将VLAN汇总成:172.16.128.0/17(172.16.128.0 255.255.128.0))

19、BGP,在ids-fw上不需要通告任何路由,因为题目没有说它上面需要通告路由

20、standby 备份的优先级是 100,默认就是,不需要改,不用设置备份的优先级

21、客户端直接登陆root用户就能进去

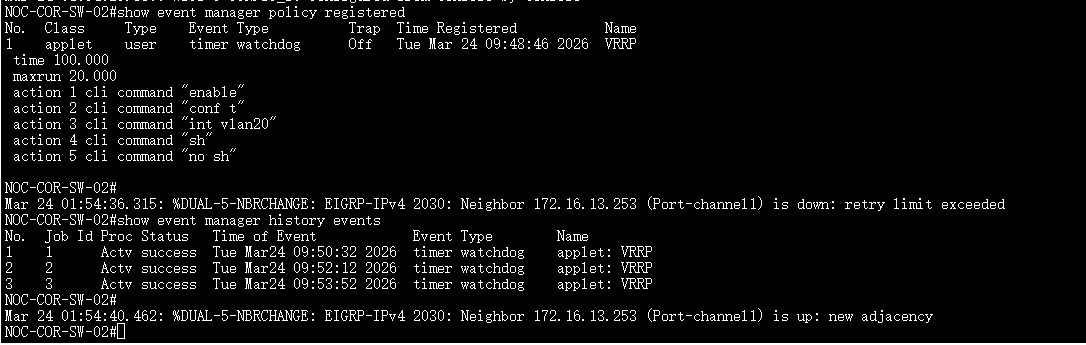
22、vrrp(vlan20) 有问题,客户端指定它为网关(.254)后,有时候ping不通,需要手动重启vlan20才能通,但是过一段时间还是通不了,因此需要配置EEM,每隔100秒自动 shutdown、no shutdown vlan接口
·踩过的坑点:
1、用户密码还是要用 al ... secret 来设置,不能直接 secret,路由器会自动转换为加密类型9,但是交换机不会,还是加密类型5
2、ASA 忘记配置 SSH对mgmt的放行(223网段)
3、ASA忘记配置 ntp时间同步
4、配置 vrf前关闭了非网管交换机,配置完成后忘记将其开启了
5、NOC-SW1 的 vtp 主服务器重启后就掉了
6、ACC-SW3 的g0/2(trunk)接口没有配置 portfast,没有配置 DTP、没有修改 native vlan
7、BR区域的路由汇总汇成了 /16位(需要汇成 /17位)
8、SH-WAN-RTR-01 上有一个 Loopback 1,忘记通告进BGP了
9、ASA 接口(Loop接口)没有配置nameif导致这条路由通告不了(通告不出去)
10、BGP SH和DJ忘记过滤iBGP邻居传入的ospf路由
11、IDS-FW忘记控制路径优先走 SH了
12、standby 备份设备的优先级是100,默认就是,不要修改就行
13、静态DAI没有 配置 static参数
14、vrrp(vlan20) 有问题,客户端指定它为网关(.254)后,有时候ping不通,需要手动重启vlan20才能通,但是过一段时间还是通不了,因此需要在 vrrp上配置EEM,每隔100秒自动 shutdown、no shutdown vlan接口
·ASA failover:
failover lan unit primary
failover lan interface FOLINK GigabitEthernet0/2
failover replication http
failover link FOLINK GigabitEthernet0/2
failover interface ip FOLINK 1.1.1.252 255.255.255.254 standby 1.1.1.253
failover ipsec pre-shared-key *****
int g0/2
 no sh
 exit
failover
1、初始化:
每台机器都要根据题目来进行更改 主机名、域名、本地用户
# 大框架:
conf t
no ip domain lo
lin con 0
logg s
exec-t 0 0
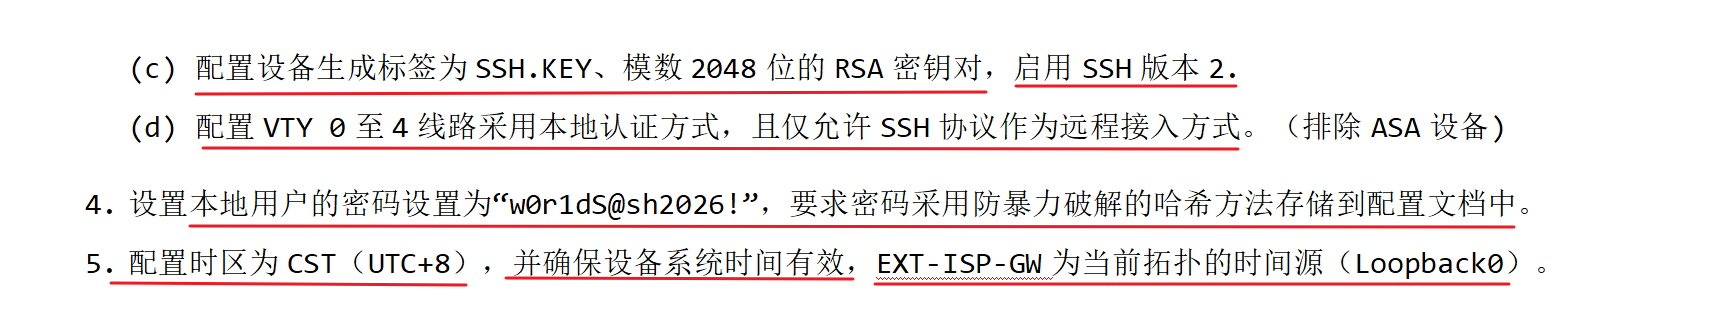
crypto key generate rsa label SSH.KEY modulus 2048
ip ssh v 2
clock timezone UTC 8
clock calendar-valid
ntp server 8.8.8.8
username extisp-sh-edge-admin privilege 15 algorithm-type scrypt secret w0r1dS@sh2026!
line vty 0 4
transport input ssh
login local
privilege level 15
exit
ip domain name ext-isp-sh-edge.cloudops.net
hostname SH-EDGE-ISP-01
do wr
ASA:
crypto key generate rsa label SSH.KEY modulus 2048
clock timezone UTC 8
domain-name dmz-fw-01.ops.net
username ids-fw-admin password w0r1dS@sh2026! privilege 15
ntp server 8.8.8.8
ssh 223.255.255.0 255.255.255.0 Mgmt //配置ssh放行Mgmt网段
wr原题:
2、vrf:
vrf definition Mgmt
 rd 2026:39
 address-family ipv4

interface GigabitEthernet1
 vrf forwarding Mgmt
 ip address 223.255.255.1 255.255.255.0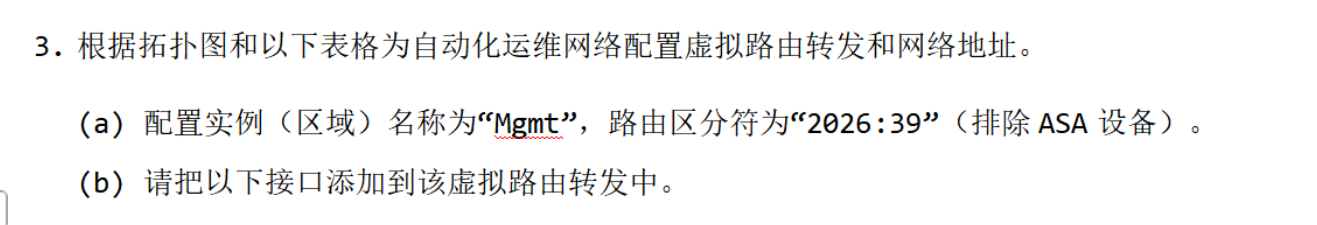
3、链路聚合、lacp 热备:
SW01为发起端,SW02为响应端(虽然题目没说)
# 需要先在物理接口配置:no switchport 才能去配置channel-group:
## SW01:
int ra g0/3,g1/0
 no switchport
 no sh
 channel-group 1 mode active

int port 1
 no sh
 ip add 172.16.13.253 255.255.255.252

## SW02:
int ra g0/3,g1/0
 no switchport
 no sh
 channel-group 1 mode passive

int port 1
 no sh
ip add 172.16.13.254 255.255.255.252不要做链路聚合热备份,会出问题
# lacp 热备:
## SW01:
int port 1
 lacp max-bundle 1

int g0/3
 lacp port-priority 65535

## SW02:
int port 1
 lacp max-bundle 1
·lacp 热备报错解决方法:
# 一条就足够:
 router eigrp 2030
 neighbor 172.16.13.253 Port-channel1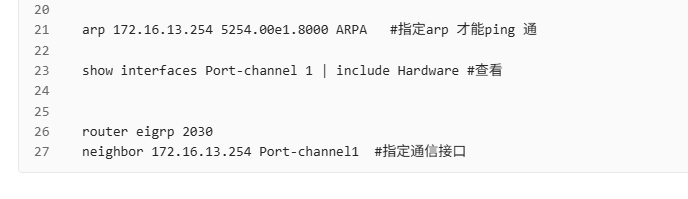
4、BVI、pppoe:
# BVI:
## RW-WAN-CORE-RT01:
bridge irb
bridge 1 protocol ieee
bridge 1 route ip

int ra g0/3-4
 no sh
 bridge-group 1

int bvi 1
 no sh
 ip add 177.78.99.150 255.255.255.252

## BR-GW-RTR-01:
bridge irb
bridge 1 protocol ieee
bridge 1 route ip

int ra g0/3-4
 no sh
 bridge-group 1

int bvi 1
 no sh

# 阻塞G0/3端口(两端都配置):
int g0/3
 bridge-group 1 path-cost 65535
# 设置 本机不选举为BVI根桥:
## 全局模式配置:
## 在RW上设置:
bridge 1 pri 65535关于PPPOE:服务端应用在物理接口上,客户端应用在BVI接口上
# PPPOE:
## RW-WAN-CORE-RT01:
username BR-GW-RTR-01 password 0 w0r1dS@sh2026!

ip local pool IP 177.78.99.149

bba-group pppoe PPPOE-FOR-BRGW
 virtual-template 4

interface Virtual-Template4
 ip unnumbered BVI 1
 peer default ip address pool IP
 ppp authentication ms-chap-v2

int ra g0/3-4
  pppoe enable group PPPOE-FOR-BRGW


## BR-GW-RTR-01:
interface Dialer4
 ip address negotiated
 encapsulation ppp
 dialer pool 4
 ppp chap hostname BR-GW-RTR-01
 ppp chap password 0 w0r1dS@sh2026!
 ppp ipcp route default

int ra g0/3-4
 pppoe-client dial-pool-number 4
interface BVI1
pppoe-client dial-pool-number 4如果获取不到地址,那就重启两端机器
5、生成树、生成树端口选举:
HQ区域的COR-SW01、COR-SW02是mstp(配置使用 VTP 同步)
COR-SW01 同时也是 mst 实例0的根桥(实例0包含所有vlan)
BR区域的ACC-SW03是 rstp
# MSTP:
## COR-SW01:
spanning-tree mode mst
spanning-tree mst configuration
 instance 1 vlan 10
 instance 2 vlan 20
spanning-tree mst 0-1 priority 0
spanning-tree mst 2 priority 4096

## COR-SW02:
spanning-tree mode mst
spanning-tree mst configuration
 instance 1 vlan 10
 instance 2 vlan 20
spanning-tree mst 2 priority 0
spanning-tree mst 1 priority 4096
·修改阻塞端口:
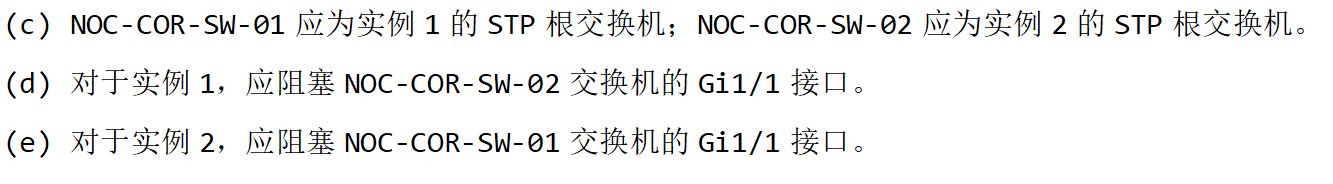
mst 1,默认阻塞 COR-SW02的G1/2,但是在ACC-SW01的G0/2上(连接COR-SW02的G1/1的端口)将cost值调大,那么原本阻塞的G1/2端口就优先于这个G1/1端口,所以G1/1端口就会被阻塞
mst 2 同理,默认阻塞的是 COR-SW01的G1/2端口..
# 生成树端口选举:
## ACC-SW-01:
int g0/1
 spanning-tree mst 1 cost 20001
int g0/2
 spanning-tree mst 2 cost 20001
6、端口安全、portfast、自动恢复:
## ACC-SW01(bpduguard):
int g0/3
 spanning-tree portfast edge
 spanning-tree bpduguard enable
 # 端口安全:
 switchport port-security
 switchport port-security maximum 2

## ACC-SW02(bpdufilter):
int g0/3
 spanning-tree portfast edge
 spanning-tree bpdufilter enable
 # 端口安全:
 switchport port-security

## ACC-SW03(bpduguard):
int g0/1
 spanning-tree portfast edge
 spanning-tree bpduguard enable
 # 端口安全:
 switchport port-security maximum 2
 switchport port-security

## 自动恢复:
errdisable recovery cause bpduguard
errdisable recovery cause psecure-violation
errdisable recovery interval 120
·要为trunk 接口配置 postfast:
# ACC-03:
int g0/2
 spanning-tree portfast edge trunk
7、snoopng、DAI:
# ACC-01、ACC-03:
## snooping:
ip dhcp snooping
ip dhcp snooping vlan 10
no ip dhcp snooping information option

int g0/*   //信任对应的上游接口
 ip dhcp snooping trust

## DAI:
ip arp inspection vlan 10
ip arp inspection validate src-mac dst-mac ip

int ra g0/1-2
 ip arp inspection trust
·对于VLAN 20要手写静态 arp acl匹配:
# ACC-SW02:
ip arp inspection vlan 20
ip arp inspection validate src-mac dst-mac ip
arp access-list DAI
 permit ip host 172.16.200.100 mac host 5254.008d.98ec
ip arp inspection filter DAI vlan 20 static    //必须要加 static参数

int ra g0/1-2
 ip arp inspection trust
8、HSRPv2、VRRPv3:
track 1 interface GigabitEthernet0/1 line-protocol
track 2 interface GigabitEthernet0/2 line-protocol
track 3 interface GigabitEthernet1/1 line-protocol
track 4 interface GigabitEthernet1/2 line-protocol

key chain HSRP-GID-191
 key 1
   key-string w0r1dS@sh2026!
   cryptographic-algorithm md5

# VLAN10(HSRPv2):
## COR-SW01:
int vlan 10
 standby use-bia
 standby version 2
 standby 191 ip 172.16.191.254
 standby 191 priority 255
 standby 191 preempt
 standby 191 authentication md5 key-chain HSRP-GID-191
 standby 191 track 1 shutdown
 standby 191 track 2 shutdown
 standby 191 track 3 shutdown
 standby 191 track 4 shutdown

## COR-SW02:
int vlan 10
 standby use-bia
 standby version 2
 standby 191 ip 172.16.191.254
 standby 191 priority 200
 standby 191 preempt
 standby 191 authentication md5 key-chain HSRP-GID-191
 standby 191 track 1 shutdown
 standby 191 track 2 shutdown
 standby 191 track 3 shutdown
 standby 191 track 4 shutdown

# VLAN20(VRRPv3):

## COR-SW01:
fhrp version vrrp v3
int vlan 20
 vrrp 200 address-family ipv4
  address 172.16.200.254
  priority 200
  track 1 shutdown
  track 2 shutdown
  track 3 shutdown
  track 4 shutdown

## COR-SW02:
fhrp version vrrp v3
int vlan 20
 vrrp 200 address-family ipv4
  address 172.16.200.254
·EEM 自动重启 vlan:
注意不要手动 run EEM,这样会导致有好多个EEM同时运行
event manager applet VRRP
 event timer watchdog time 100
 action 1 cli command "enable"
 action 2 cli command "conf t"
 action 3 cli command "int vlan20"
 action 4 cli command "sh"
 action 5 cli command "no sh"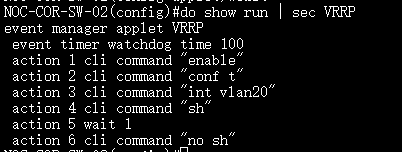
执行记录: